Widely trusted tools like ConnectWise ScreenConnect and AnyDesk may be abused by attackers, and when left unattended, they can present a problem: Their legitimate prevalence makes attacker activity harder to spot, and any vulnerabilities affecting them can turn a trusted platform into an infection vector.
Stay ahead with intelligence-driven cyberthreat research and reporting
November 11, 2026
Remote access hardening playbook: Reducing RMM tool risk for SMBs
November 11, 2026
Every PC has a junk drawer, and attackers know it
New Acronis research reveals how outdated software, unsupported apps and delayed security updates create hidden risks for SMBs and MSPs.
November 10, 2026
The remote access blind spot: An analysis of RMM tool risk for SMBs
Remote monitoring and management (RMM) tools are widely used in modern IT operations, but they are increasingly exploited by cybercriminals. Here, in this first blog, in a two-part series, we analyze the data to discover where RMM-associated risks lie.
November 04, 2026
BOSSAI: Inside the AI attack mesh that targeted Taiwan’s emergency services
Acronis TRU reveals how one operator used a 12-agent AI attack mesh to target organizations across 11 countries and transform cyberthreat operations.
October 29, 2026
Configured to protect: How to properly use security policies
Buying protection is not the same as being protected. What decides the outcome is how the protection is configured and used every day. This report looks at that gap. It uses the live configuration records behind a large managed fleet, more than 1.6 million active endpoints, to see how protection plans are actually set up, how administrators and the providers who manage them choose to structure plans and what those choices tel
October 28, 2026
Inside Qilin ransomware: ESXi attacks, affiliate networks and double extortion
Qilin, also known as Agenda, is a Russian-speaking ransomware-as-a-service (RaaS) operation that first appeared in 2022.
Threat Research Unit events
December 01, 2026, 7:00 PM (GMT+0)
The AI paradox: A playbook for managing AI threats by harnessing AI's potential
New fear meets new gear: Put AI to work for your cyber defense. AI is changing the game for both sides on cybersecurity. Threat actors can launc...
English
1 hour
Webinar on demand
Identity under attack: The MSP's guide to closing Microsoft 365 and Entra ID protection gaps
See how MSPs can reduce Microsoft 365 identity risks, strengthen security posture and recover critical Entra ID assets with Acronis.
English

Webinar on demand
From immutable storage to clean recovery: Building OT cyber resilience from the ground up
Discover how leading OT security and cyber resilience experts protect industrial operations from modern cyberthreats Cyberattacks against oper...
English
Webinar on demand
Deliver MDR, Not SOC Complexity: A Practical Demo for MSPs
In this live demo webinar, you’ll discover how Acronis MDR closes that gap by combining 24/7 SOC expertise with integrated detection, response, recovery and patching on a single platform.
English
Webinar on demand
Rewriting the ransomware playbook: The new rules of threat protection in the AI era
Watch a LIVE attack demo and learn how to prevent, detect, respond to and recover from AI-powered ransomware attacks
English
Meet our speakers at upcoming events
AVAR 2026
AVAR 2026 agenda2nd to 4th December 2026 | Hyderabad, India
From Open Directories to AI-Coded Malware: How a Pakistan-Nexus Threat Actor Leaked Their Entire Arsenal Targeting Afghan Telecom and South Asian Critical Infrastructure
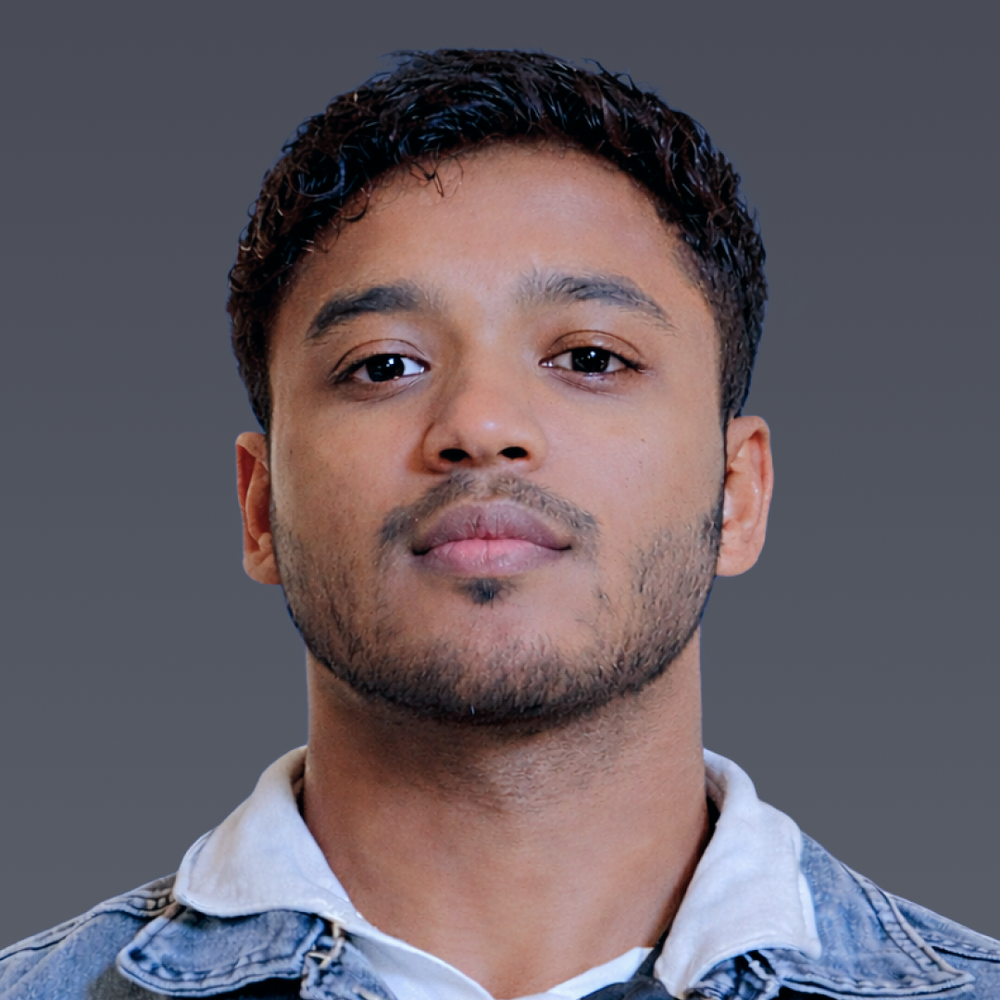
Subhajeet Singha
Subhajeet works around threat intelligence, malware research, and reverse engineering. Subhajeet actively investigates advanced persistent threats (APTs), reverse-engineers complex malware strains, and contributes to research initiatives that improve threat detection.