Achieve DORA compliance with Acronis

Achieve DORA compliance with Acronis

Acronis delivers the solutions financial institutions and their service providers need to stay compliant.

How does DORA relate to cybersecurity?

The Digital Operational Resilience Act (DORA) is an EU regulation that focuses on IT risk management in the financial sector. DORA applies to financial entities such as banks, insurers and investment firms, as well as to information and communication technology (ICT) service providers, including managed service providers (MSPs), cybersecurity firms, cloud platforms, data centers and SaaS vendors.

DORA cybersecurity pillars

Operational resilience

Operational resilience

Implement ICT risk management frameworks and incident reporting protocols. Ensure the ability to recover data and restart systems quickly after an incident.
Cybersecurity provisions

Cybersecurity provisions

Specify how the financial institution and its service providers will be able to quickly identify and mitigate potential security issues.
Establish continuous monitoring

Establish continuous monitoring

Build cross-functional collaboration among IT teams and service providers so there is clarity around contractual agreements. Ensure continuous monitoring of the financial institution’s systems.

What are the consequences of failing to comply with DORA?

Enforcement of DORA began in 2025. Both financial institutions and service providers can be subject to financial penalties for non-compliance.

Financial entities can face periodic penalty payments of up to 1% of their average daily global revenue for up to six months. Service providers, including MSPs, can incur similar penalties. Additionally, individuals responsible for the breach can also face fines. Organizations that comply with DORA will not only avoid penalties but also strengthen their cybersecurity posture and gain a competitive edge in the market.

What are some of the common challenges of DORA compliance?

DORA presents a set of unique and difficult challenges for financial institutions and their service providers, including:
  • Fragmented IT visibility and response mechanisms: Many firms lack centralized frameworks for evaluating ICT risks across departments, making it difficult to identify vulnerabilities before they escalate.
  • Manual, time-consuming audit documentation: Meticulous record keeping is required for DORA compliance. Compliance teams often spend months manually sorting through contracts, reviewing security protocols and identifying gaps. AI-driven solutions can enable teams to simplify and speed up those processes.
  • The unclear division of responsibility between teams and providers: Financial institutions remain accountable for third-party failures, even if an external provider is responsible for the failure itself. It’s essential for financial institutions to establish clear contractual agreements and continuous monitoring processes.
What are some of the common challenges of DORA compliance?

How Acronis supports DORA compliance

With Acronis, financial institutions and their service providers can enhance their operational resilience, improve incident response and maintain compliance with DORA requirements, including:

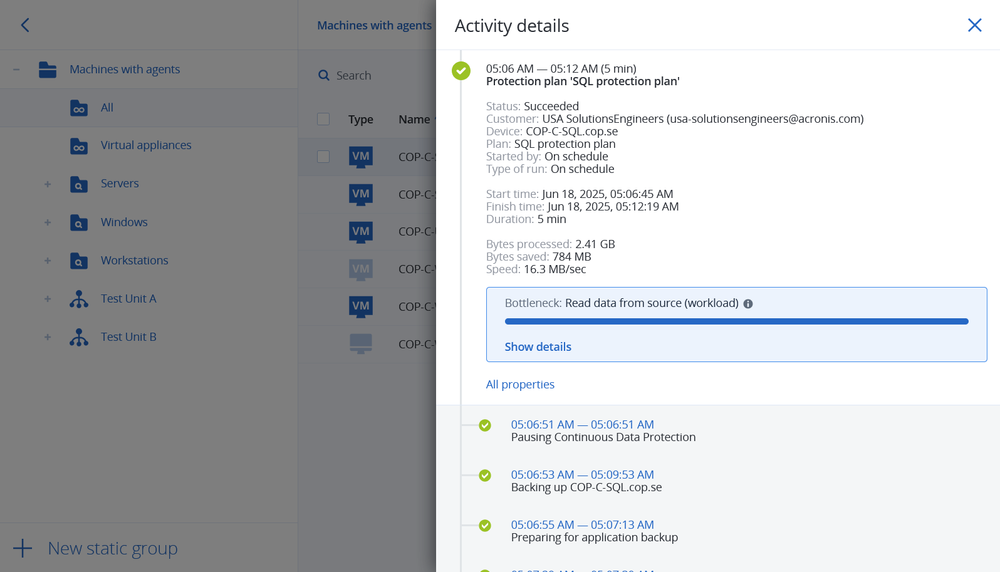
Enable rapid system restoration and recovery of data in disparate environments

Acronis delivers automated backup and fast recovery across physical, virtual and cloud environments. This helps financial entities and MSPs restore critical data, maintain business continuity and meet DORA resilience requirements.
Enable rapid system restoration and recovery of data in disparate environments

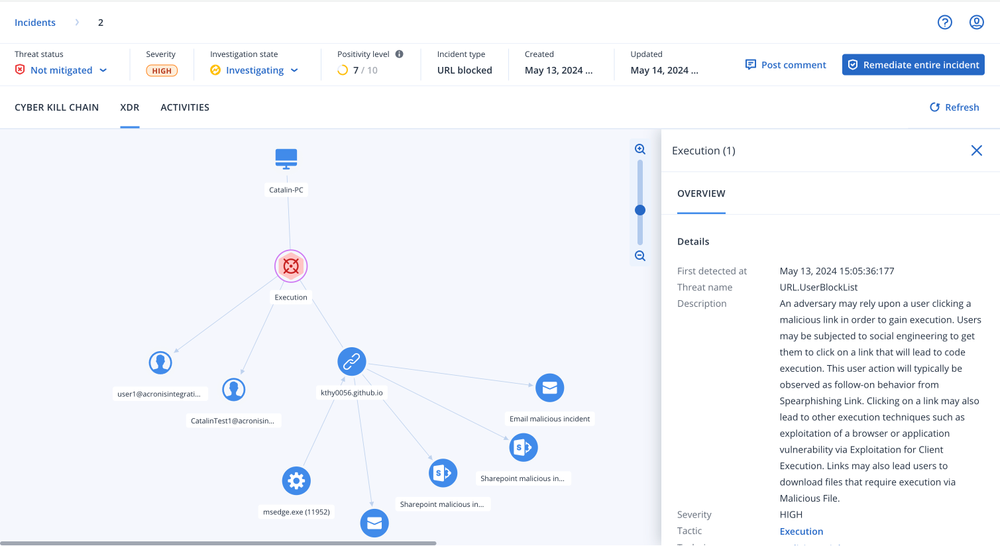
Stop incidents before they start with cybersecurity at the heart of operations

Acronis delivers natively integrated cybersecurity solutions in a single dashboard, giving MSPs and IT teams full visibility into risks, alerts and reports. This unified, AI-powered platform simplifies issue detection, rapid response and audit documentation, helping organizations meet key DORA cybersecurity and compliance requirements.
Stop incidents before they start with cybersecurity at the heart of operations

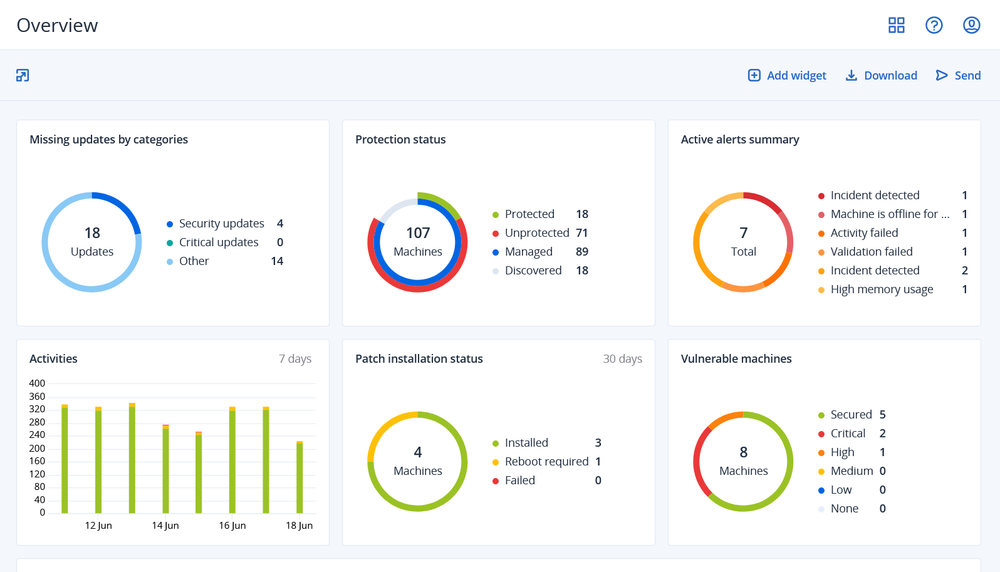
Get everybody working together in harmony and alignment with MSPs

By providing a single platform for managing data protection, cybersecurity and endpoint management, Acronis enables simplified cross-functional collaboration. Both internal teams at financial institutions and MSPs can easily comply with DORA’s requirements for clear contractual agreements and continuous monitoring processes.
Get everybody working together in harmony and alignment with MSPs
Acronis Compliance Navigator
See the full mapping to discover how Acronis can help you meet DORA requirements

Sorry, your browser is not supported.

It seems that our website is incompatible with your current browser's version. Don't worry, this is easily fixed!
To view our complete website, simply update your browser now or continue anyway.