ISO 27001 helps organizations manage information security in a more disciplined, repeatable way. Built around an information security management system, it gives businesses a risk-based framework to identify what matters, apply the right safeguards, review performance and improve over time. Globally recognized and certifiable, it is often used to show customers, partners and stakeholders that security is being managed in a structured, auditable way.
ISO 27001 is broader than technology alone, but technology still plays a major role in how information security is put into practice. For organizations evaluating tools and platforms, the technological control areas are often the most relevant part of the standard because they relate to day-to-day security across systems, users, devices, and data.
How does ISO 27001 relate to cybersecurity?
What happens if you do not meet ISO 27001?
ISO 27001 is not a fine-based regulation for most organizations, but falling short can still have real business impact. Certification may be delayed or denied, remediation work can expand, and customer or stakeholder conversations can become harder where independent assurance is expected.
How Acronis helps
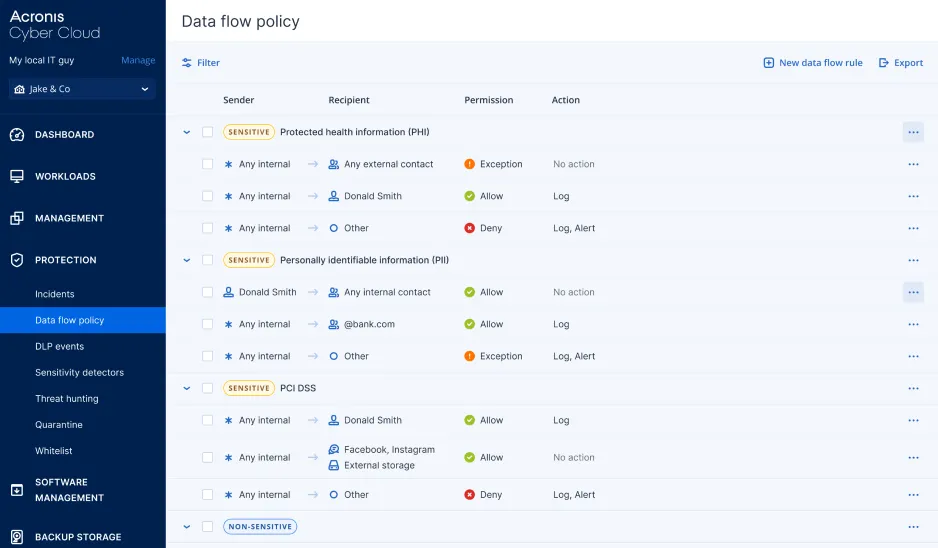
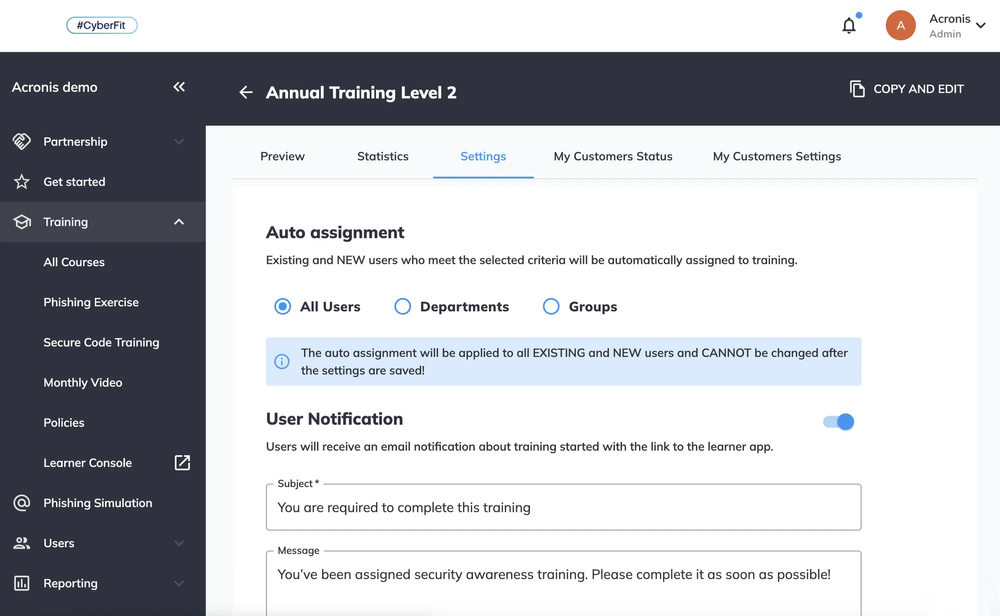
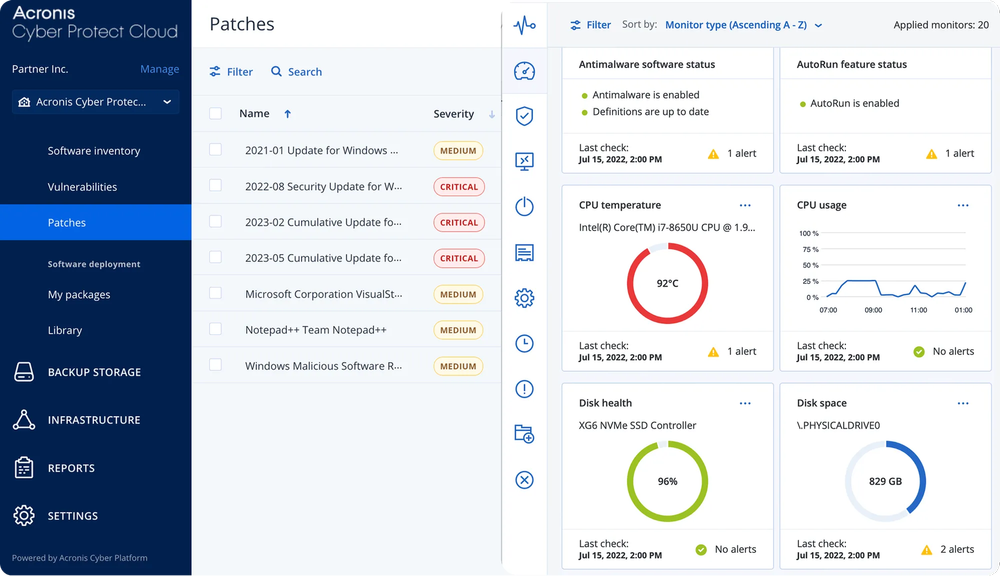
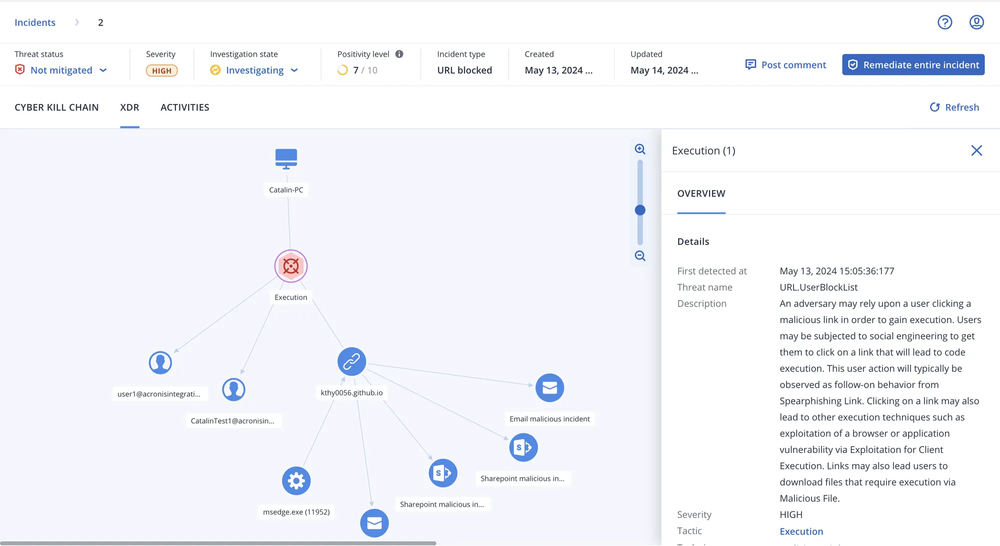
Acronis can support selected areas that may form part of a broader ISO 27001 program. That can include capabilities related to data protection, user awareness, system maintenance and threat detection and response.
Acronis Compliance Navigator
Frequently asked questions
Sorry, your browser is not supported.
It seems that our website is incompatible with your current browser's version. Don't worry, this is easily fixed!
To view our complete website, simply update your browser now or continue anyway.