Acronis Compliance Navigator
How does NIS 2 relate to cybersecurity?
Europe’s Network and Information Systems Directive (NIS 2) aims to enhance and standardize a high level of cybersecurity across the European Union. This mandate places new security and reporting requirements on key sectors, including energy, transportation, health care, banking and other critical infrastructure industries.
NIS 2 fines and penalties
Non-compliance with NIS 2 can result in heavy fines, regulatory investigations, and legal action. Beyond the financial impact, it can damage an organization’s reputation and erode customer trust. Managed service providers may also face added pressure, as clients look to them to ensure systems and data stay compliant.
- Up to €10 million or 2% of global annual turnoverEssential entities
- Up to €7 million or 1.4% of global annual turnoverImportant entities
How Acronis helps
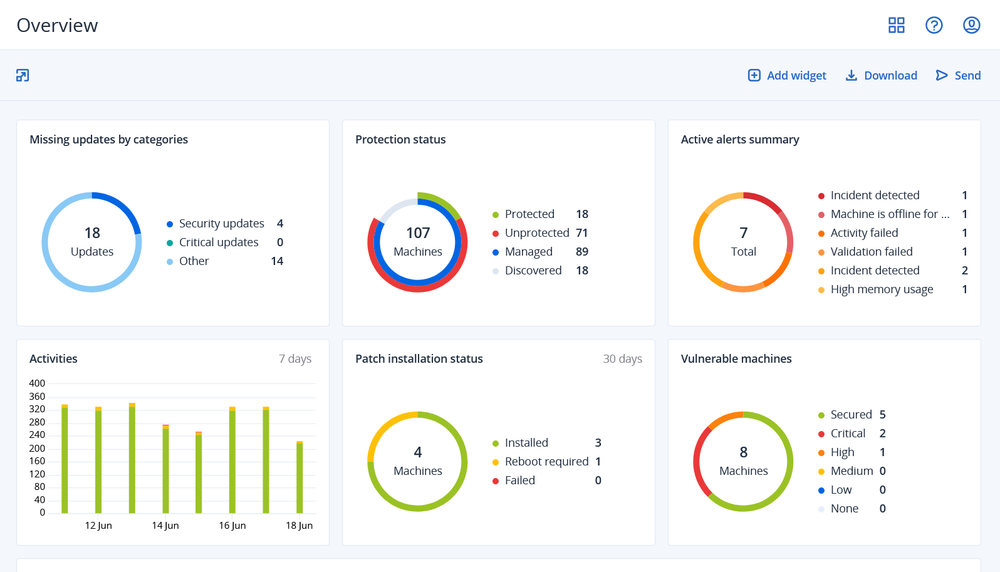
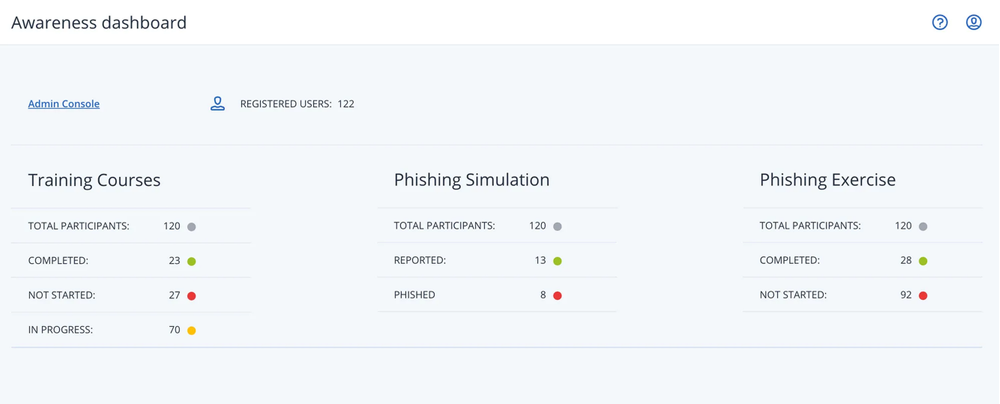
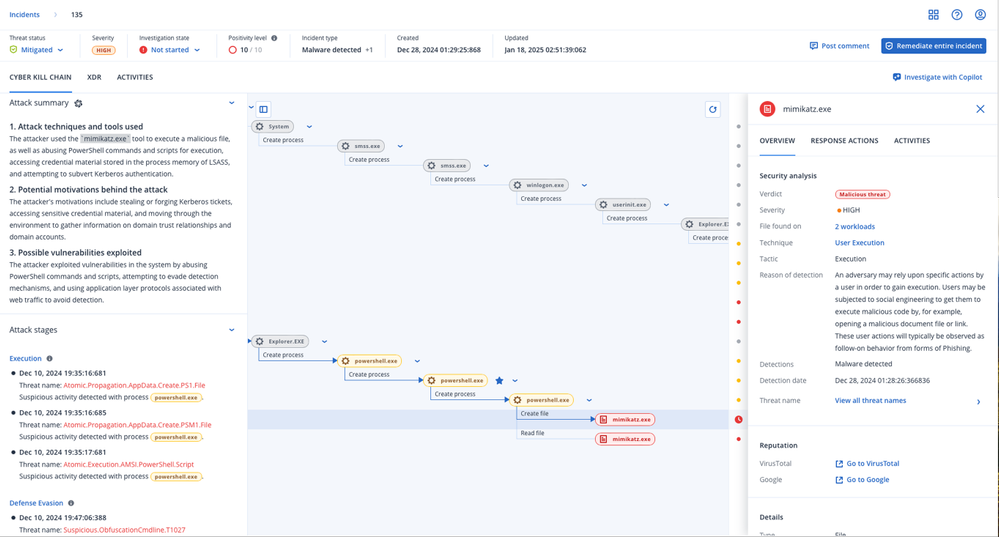
Acronis helps organizations meet core NIS 2 requirements with natively integrated protection with compliance-enabling solutions. See some of the ways Acronis can help you meet NIS 2 requirements.
NIS 2 resources
- DatasheetDrive NIS 2 compliance for your clients with confidence
- White paperNIS 2 Directive on cybersecurity for MSPs
- White paperIs your business ready for NIS 2 compliance?
- White paperNIS 2: A guide to navigating Europe’s confusing yet powerful directive
- On-demand webinarMSP compliance in the age of AI — NIS 2, cyber insurance and beyond
- On-demand webinarStop ransomware attacks and meet NIS 2 requirements with Acronis Cyber Protect
Looking for help?
Frequently Asked Questions

Sorry, your browser is not supported.
It seems that our website is incompatible with your current browser's version. Don't worry, this is easily fixed!
To view our complete website, simply update your browser now or continue anyway.