NIST 2.0 essentials and how Acronis helps

NIST 2.0 essentials and how Acronis helps

NIST CSF 2.0 gives organizations and MSPs a flexible, proven framework to manage cyber risk, boost resilience and strengthen overall security posture.

How does NIST framework relate to cybersecurity?

NIST 2.0 offers a taxonomy of high-level cybersecurity outcomes that can be used by any organization to better understand, assess, prioritize and communicate its cybersecurity efforts. The framework helps guide investment and strategy through six core functions that can be applied to all types of environments, including cloud, mobile and artificial intelligence systems.

NIST 2.0 cybersecurity pillars

  • Govern

    Govern

    The organization’s cybersecurity risk management strategy, expectations, and policy are established, communicated, and monitored.
  • Identify

    Identify

    The organization’s current cybersecurity risks are understood.
  • Protect

    Protect

    Safeguards to manage the organization’s cybersecurity risks are used.
  • Detect

    Detect

    Possible cybersecurity attacks and compromises are found and analyzed.
  • Respond

    Respond

    Actions regarding a detected cybersecurity incident are taken.
  • Recover

    Recover

    Assets and operations affected by a cybersecurity incident are restored.

Why is NIST 2.0 important?

The NIST 2.0 CSF provides a systematic and measurable approach to cybersecurity. It helps organizations to define their cybersecurity posture as well as set goals to establish better protection. With a common frame of reference, organizations can share benchmarks and strategies, as well as assess risk management practices.

Why follow NIST 2.0?

Most critically, for credibility. NIST 2.0 helps organizations show external stakeholders, including business partners and prospective clients, that they’re committed to data protection and cybersecurity. Organizations can make better decisions about risk and prioritize cybersecurity activities to reach critical goals.
Why follow NIST 2.0?

How do organizations usually fall short of NIST 2.0 alignment?

Efforts to follow NIST 2.0 often reveal common gaps across key framework functions, including:
  • Identify: Limited asset visibility causes many organizations to fall short in this category. Organizations that fail to fully understand their data, hardware, software and systems cannot meet this function.
  • Protect: Organizations often struggle with this function because they lack a proper layered defense strategy. Without strong protection in place, critical assets are left open to attacks and data theft. This also means systems and software can't support effective risk management.
  • Detect: Organizations that have weak logging and detection capabilities will fall short in this function. Without adequate detection capabilities, they often fail to find and analyze anomalies that could signal a cybersecurity incident.
  • Respond and Recover: The result of slow recovery and unreliable backup isn’t just a failure to satisfy the Respond and Recover functions of NIST 2.0. Weak recovery capabilities can also lead to prolonged downtime and more severe impacts when attacks do succeed.
How do organizations usually fall short of NIST 2.0 alignment?

How does Acronis help organizations align with NIST 2.0?

With Acronis, organizations can effectively align with NIST 2.0 and reduce the complexity of their cybersecurity posture.

Know what’s running in your system, improve protection with asset visibility

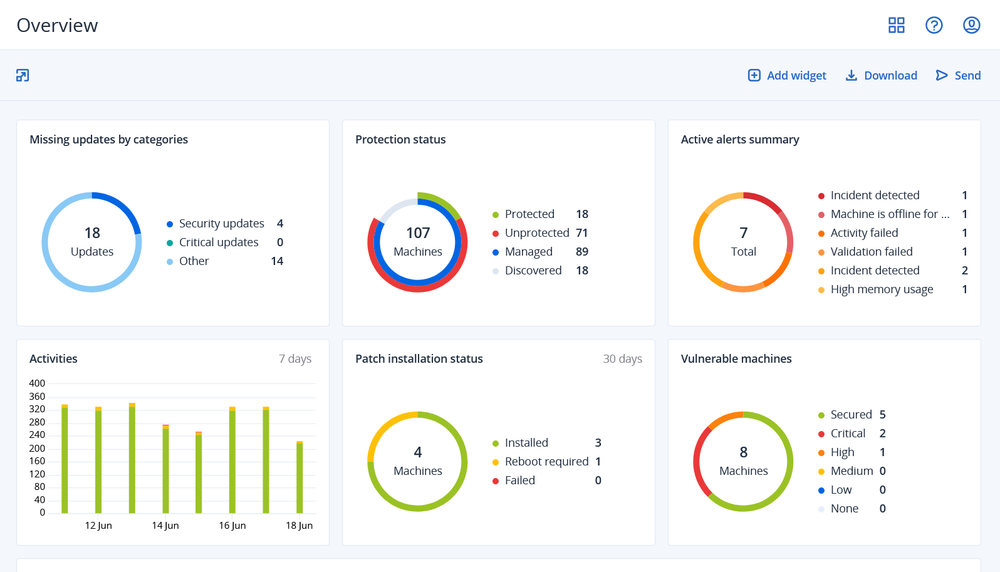
By consolidating multiple solutions into a single, unified platform, Acronis eliminates the need to manage multiple point solutions. The single dashboard simplifies management and offers centralized visibility and control, so organizations can audit their systems and easily inventory the tools in their technology stacks.
Know what’s running in your system, improve protection with asset visibility

Improve protection for your organizations or your clients with integrated solutions

Acronis offers EDR, backup, disaster recovery and AI-powered capabilities for detecting and preventing cyberattacks, empowering organizations to practice defense in depth through one platform manageable through a single interface. The natively integrated Acronis platform enables organizations to implement far deeper cybersecurity protection than they can with individual point products.
Improve protection for your organizations or your clients with integrated solutions

Use the power of AI to identify and prevent threats before they do damage

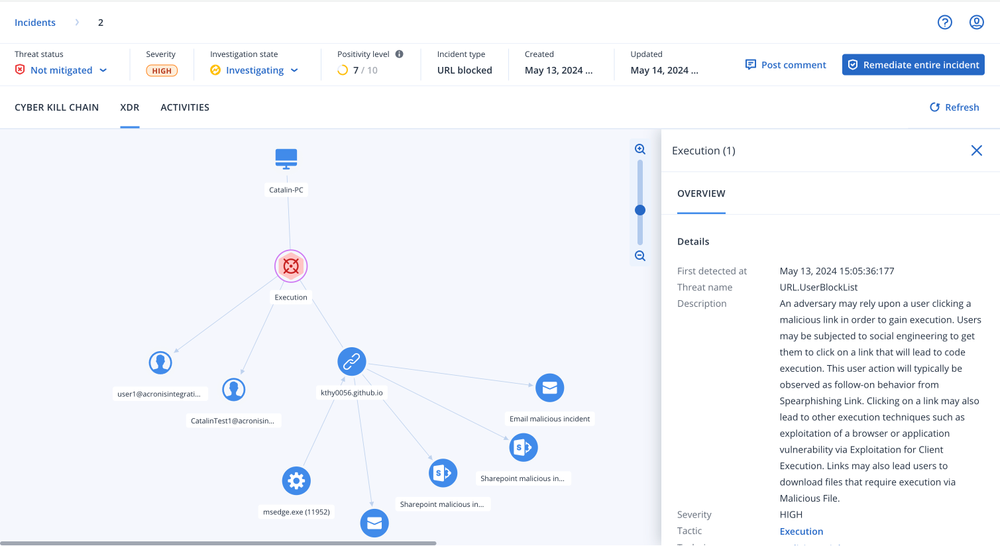
The Acronis platform offers powerful AI-enabled capabilities to investigate, shut down and catalog the sources of potential cyberattacks. Organizations can stop damage from attacks before it starts and know which sources are susceptible to launch attacks.
Use the power of AI to identify and prevent threats before they do damage

Ensure data is protected and available, respond easily with rapid recovery

Acronis backup and disaster recovery keep data safe and available. Organizations can bounce back easily and quickly from incidents of any kind, including disasters, cyberattacks or other unplanned outages. A nonexpert can recover data and get a system up and running again with just one click.
Ensure data is protected and available, respond easily with rapid recovery
Acronis Compliance Navigator
Turn NIST 2.0 into action. View Acronis’ full product mapping to the framework

Sorry, your browser is not supported.

It seems that our website is incompatible with your current browser's version. Don't worry, this is easily fixed!
To view our complete website, simply update your browser now or continue anyway.