Fortinet FortiGate


Company:
Fortinet
Integration:
Fortinet FortiGate
Category:
EDR & XDR
Acronis

Fortinet FortiGate integration with Acronis Cyber Platform

Acronis and Fortinet have partnered to deliver complete, natively integrated protection, accessible for organizations of any size and specifically built for MSPs.

With the integration of Acronis Advanced Security + XDR and FortiGate Next-Generation Firewall (NGFW), service providers can easily and quickly prevent, detect, analyze, respond to, and recover from incidents across the most vulnerable attack surfaces.

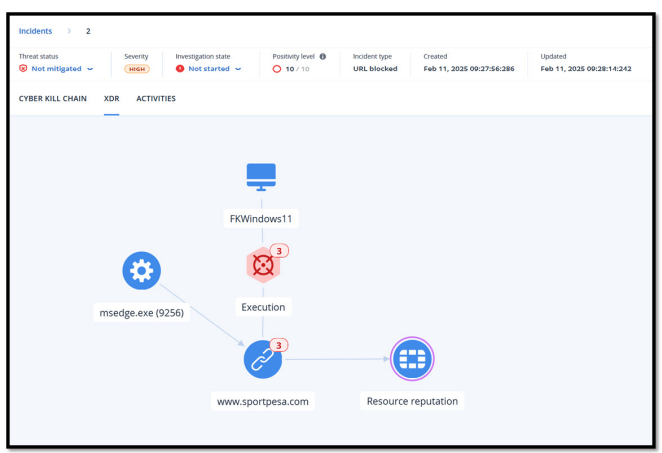
Enrich your Extended Detection and Respond (XDR) incidents with URL and IP address reputation for enhanced visibility when investigating network threats.

With this integration, MSPs can initiate various response actions to remediate malicious changes and prevent future attacks from network-based threats.

FortiGate and Acronis Integration: Use Cases

Swiftly react to network-based security threats with Fortinet’s intelligence. Security analysts can leverage Fortinet’s advanced threat intelligence capabilities to obtain a verdict more quickly and easily,centrally accessing specific details of any network artifact detected by Acronis Cyber Platform XDR.

Expand response capabilities by enabling corporate-level blocking of any network threat using FortiGate NGFW. Prevent recurring threats, massive malware infections, or APT group campaigns. This blocking can be adapted to eachcompany’s network architecture, allowing the selection of policy or policies that will be used for the blockings.

Extend visibility, protection, and response to the most vulnerable attack surface. Correlate data from FortiGate NGFW and Acronis XDR to get visibility and response capabilities across multiple attack vectors,including endpoints, email, identity, networks, and Microsoft 365 apps.
FortiGate and Acronis Integration: Use Cases

Features

  • Enhance visibility into security incidents originating from network-based threats

    Malware threats detected in XDR incidents are automatically referenced against the Fortinet network addresses reputation databases. XDR incident details are automatically enriched with metadata provided by Fortinet, enabling your analyst to investigate and take corrective actions to prevent future attacks.

  • Variety of remediation and preventive actions available

    Through Advanced Security + XDR integration with Fortinet you can initiate various response actions, such as blocking suspicious IP addresses or URLs to prevent future attacks from these malicious addresses. This integration also enables you to isolate the infected device from the network to prevent the spread of the attack. XDR response actions initiated on Fortinet are visible within the XDR incident details, enabling you to keep track of all actions taken on these incidents.

FortiGate Next-Generation Firewall NGFW

Fortinet Support

Discover the Acronis Technology Ecosystem

Explore how Acronis partners with top technologies to deliver secure, integrated, and automated solutions. Stay informed and unlock new opportunities through our growing ecosystem.

New Case Study

Nord Security business suite accelerates product adoption by 350% through the Acronis Technology Ecosystem

Read now