LogRhythm Axon is a cloud-native SIEM platform built for security teams that are stretched thin by immense amounts of data and an ever-evolving threat landscape. LogRhythm Axon’s powerful security analytics, intuitive workflow, and simplified incident response gives analysts contextual insight into cybersecurity threats so they can reduce noise and quickly secure the environment.
Acronis Cyber Platform integration with LogRhythm SIEM
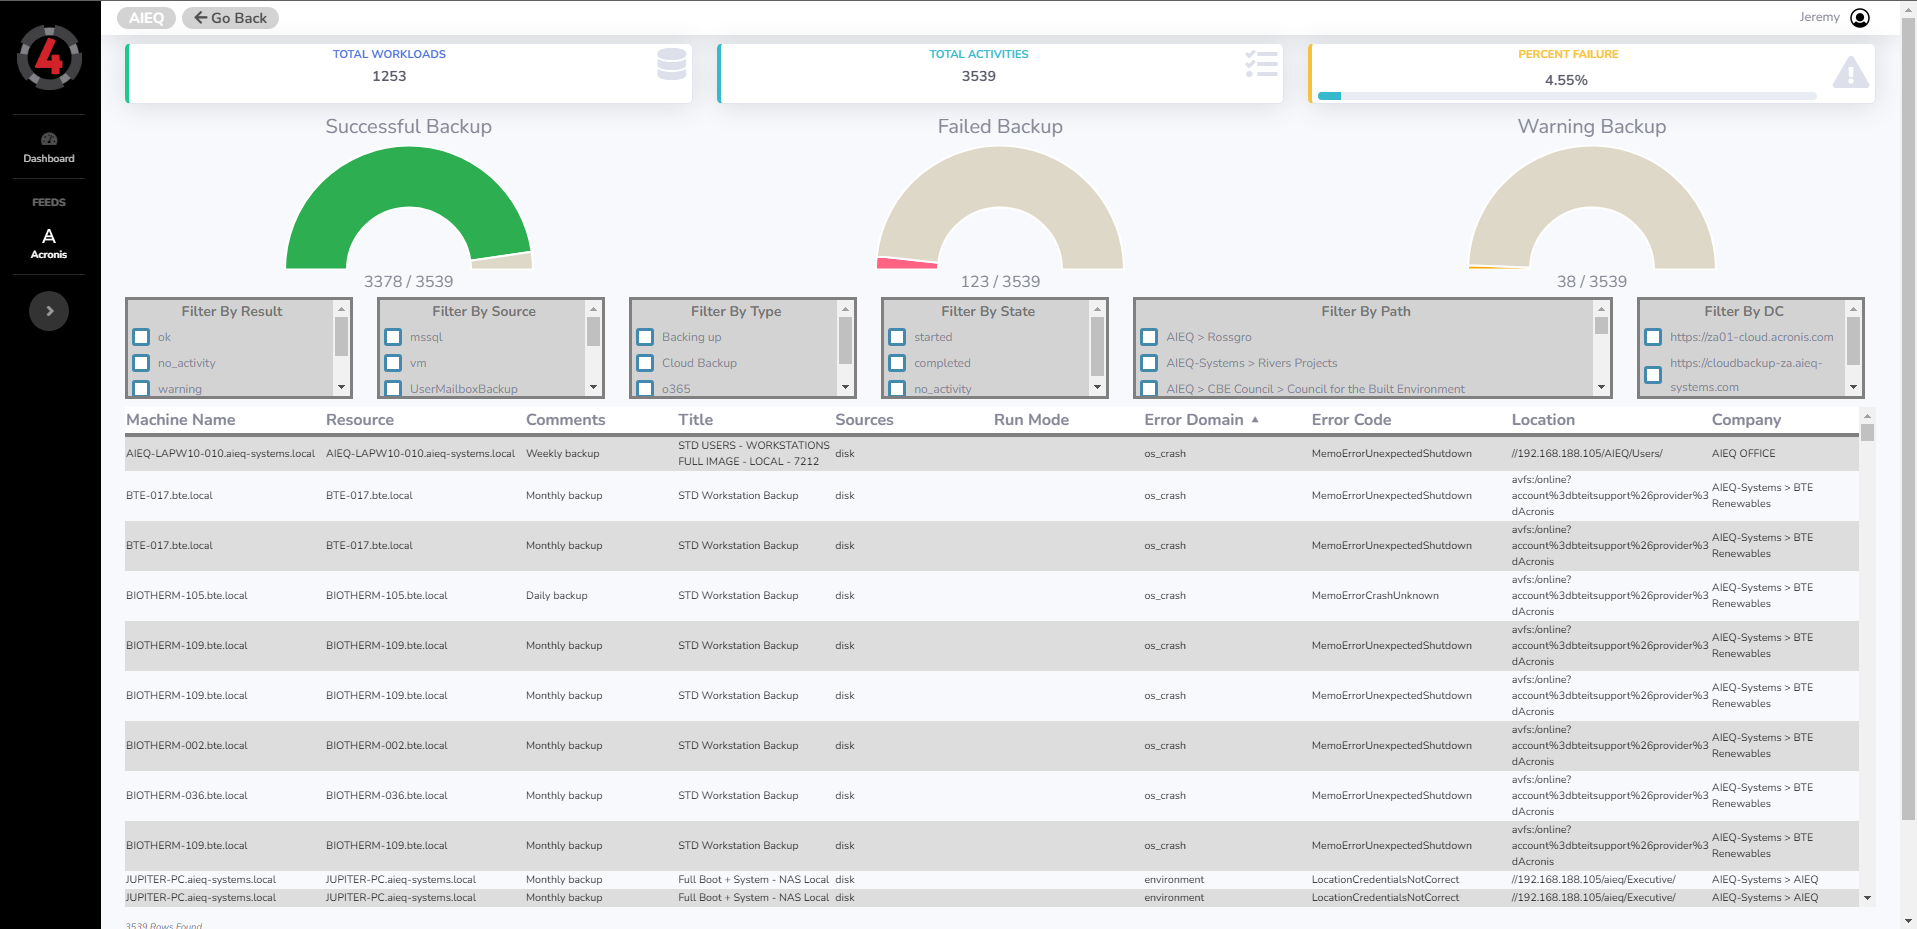
LogRhythm SIEM allows MSPs to perform security incident investigation and threat hunting. Integrating Acronis Cyber Platform as additional data source, enables MSPs to collect more telemetry and enrich existing telemetry with detections from Acronis Advanced security, while keeping Acronis as a crucial service monitored for dangerous events.
Explore resources
Cloud SIEM Made Easy
Features
Save time
An open cloud-native SIEM platform alleviates time spent managing and maintaining infrastructure while easily integrating with other applications.
Gain comprehensive visibility
Automatically collect data from SaaS, self-hosted cloud, and on-prem agents. Metadata extraction combined with easy-to-use tools to build custom parsers ensures visibility across the environment in a centralized console.
Find threats faster
Search driven widgets and intuitive dashboards make it easier to find information and respond to threats. Ensure threat detection engineering with the ability to test your analytics rules.
Execute seamlessly
Surface critical threats and secure your environment with powerful security analytics and simplified incident response. Leverage out-of-the-box content or author your own custom content.
Support of core event format
Acronis supports core event format - CEF (Common Event Format), enabling MSPs to work with the data sent by the integration out of the box. Alerts are pre-formatted on Acronis side and don't require MSP to create any additional rules on SIEM side.
Simple integration enablement
It's very easy to enable the integration by providing server and client certificates, establishing connection to the dedicated syslog server and specifying the server port.
Threat hunting across all managed companies
Integration allows MSPs to select which customer tenants in Acronis should send alerts to SIEM. Since alerts are sent to the same SIEM instance, it's possible to run correlation, threat hunting and perform investigation for all customers in the same console. It also empowers MSPs to search for threats, that were discovered on one workload in one customer tenant, in other customers environments.
Select data you want to see
It is possible to select which alerts should be sent to SIEM. With this functionality, MSPs benefit from reducing the amount of alerts sent to SIEM and, therefore, lower storage consumption. MSPs can select and work only with the data that is necessary.