The Acronis Cyber Platform integration brings EDR incidents, alerts, workload inventory, protection-plan posture and Windows endpoint telemetry into Mars Security. MSPs use it to turn new threat campaigns into hunts across Acronis-protected workloads, get a clear outcome for every hunt and see where detection coverage has gaps.
Mars Security integration with Acronis Cyber Platform
Mars Security integrates with Acronis Cyber Platform to help managed service providers (MSPs) hunt threats and engineer detections across every client workload Acronis protects. Prevention will fail, and AI-driven attacks move faster than a reactive SOC. Detection decides the outcome. Mars is a threat hunting and detection engineering platform your security team runs on the stack it already owns, including Acronis Cyber Platform. Mars queries data where it lives.
- No data ingestion.
- No tool replacement.
- Your team stays in control.
Intelligence-driven hunts
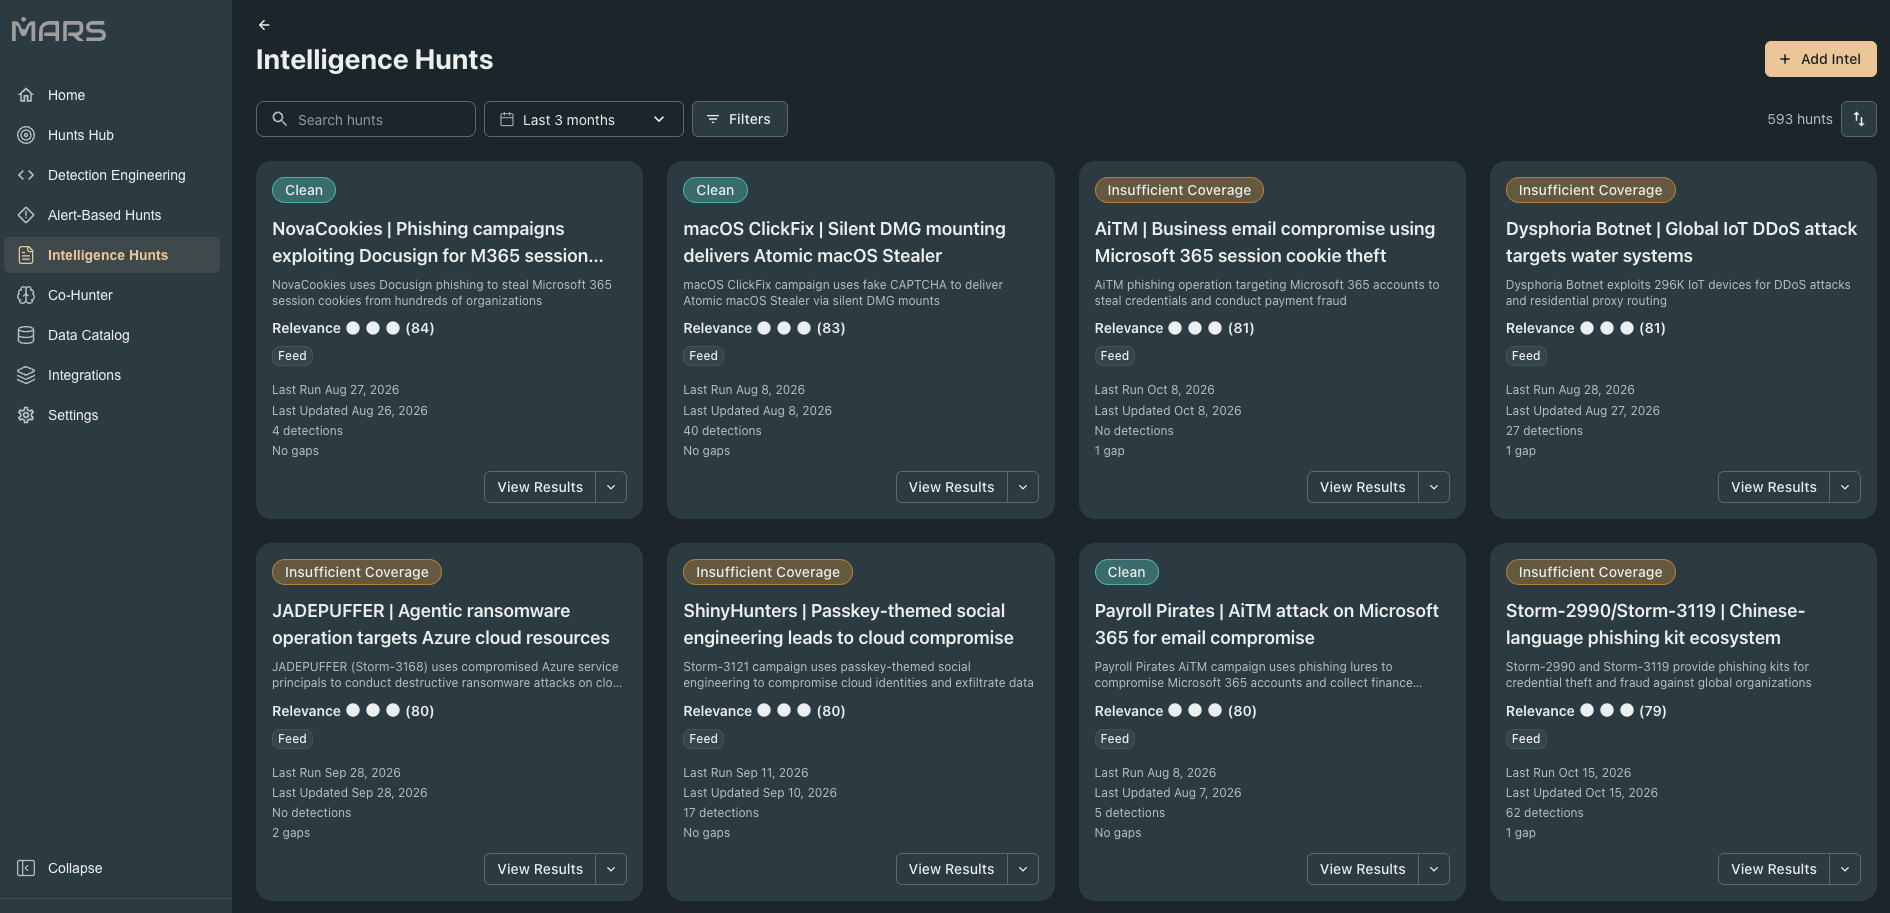
- Mars tracks new threat campaigns as they are published, scores each one for relevance to your environment, extracts the TTPs and hunts for them across your data, including Acronis EDR incidents, alerts and endpoint telemetry. Every hunt returns a clear outcome (clean, benign, suspicious or threat detected) and shows whether your detections cover the campaign or leave a gap. Detection engineering
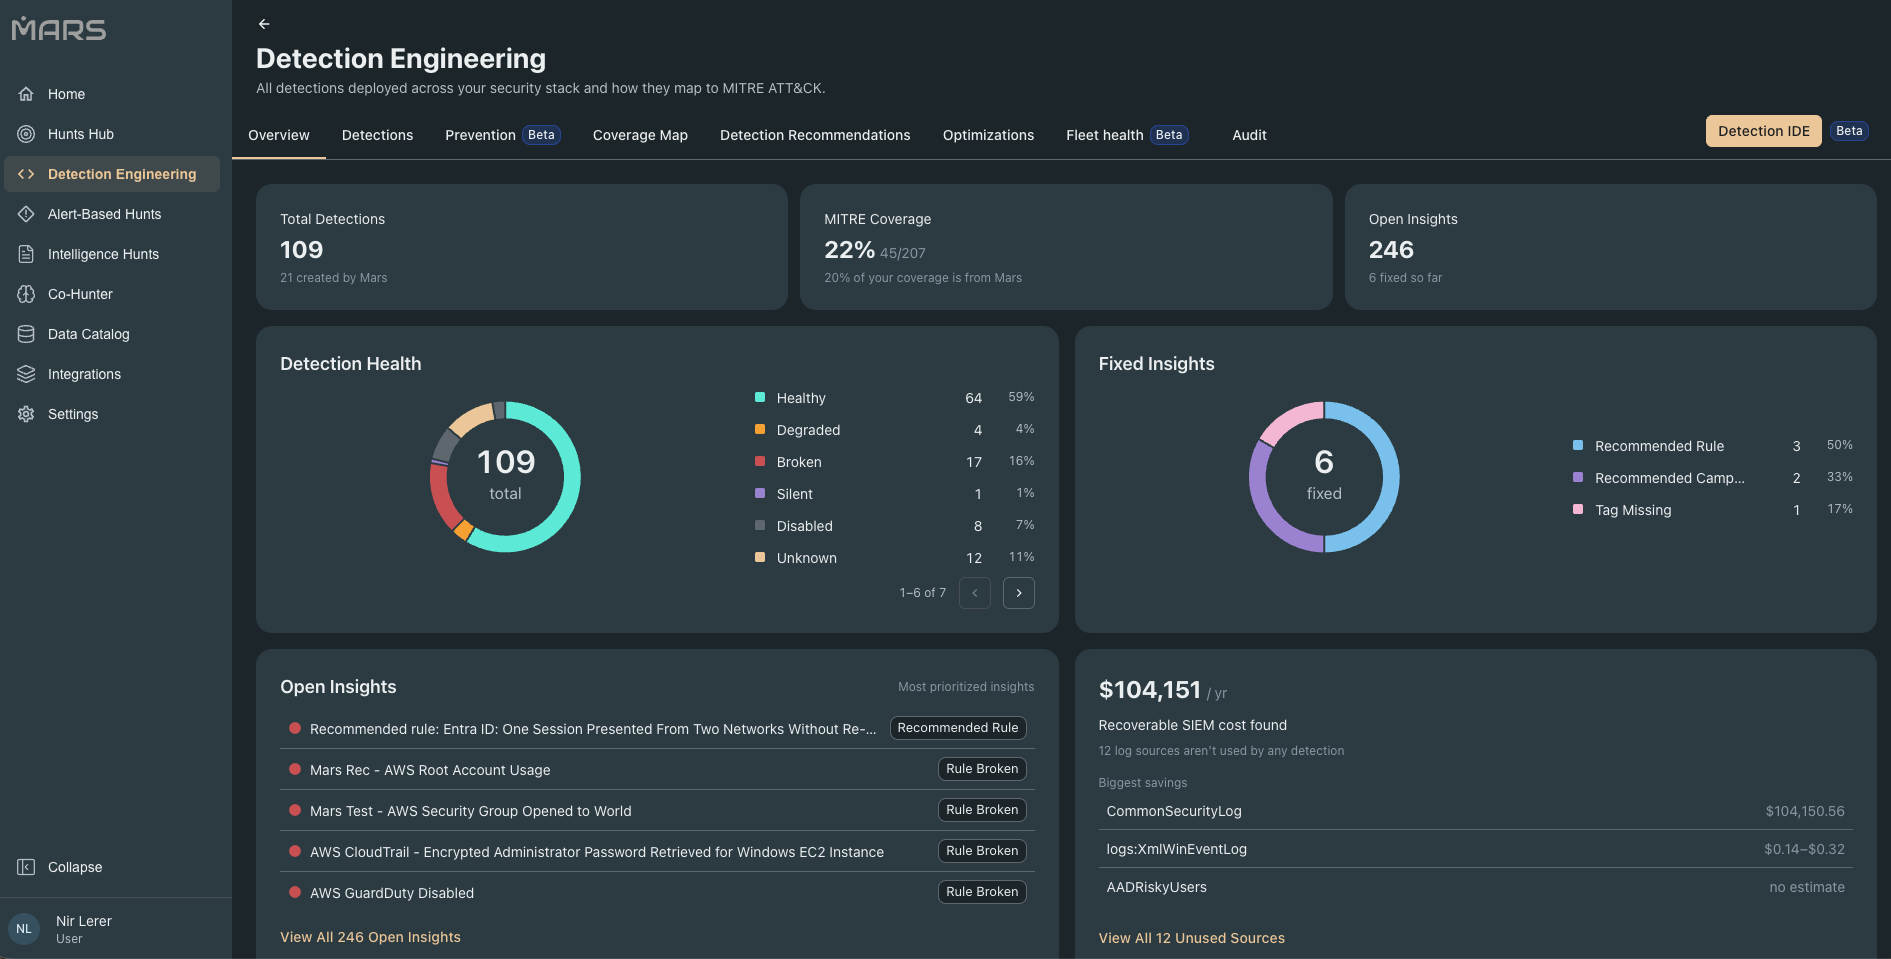
- Mars maps your rules to MITRE ATT&CK and grades the health of each one: healthy, degraded, broken, silent or disabled. It recommends the detections you are missing, including cross-campaign rules for techniques shared by several campaigns, writes them in your SIEM or EDR’s native language and pushes them to production. Scheduled playbooks and alert-based hunts
- Run recurring hunting playbooks, such as endpoints missing EDR coverage, over-provisioned identities or access from unmanaged devices. Mars also turns alerts into hunts, including Acronis EDR alerts and incidents, and investigates them across sources. Works with your stack
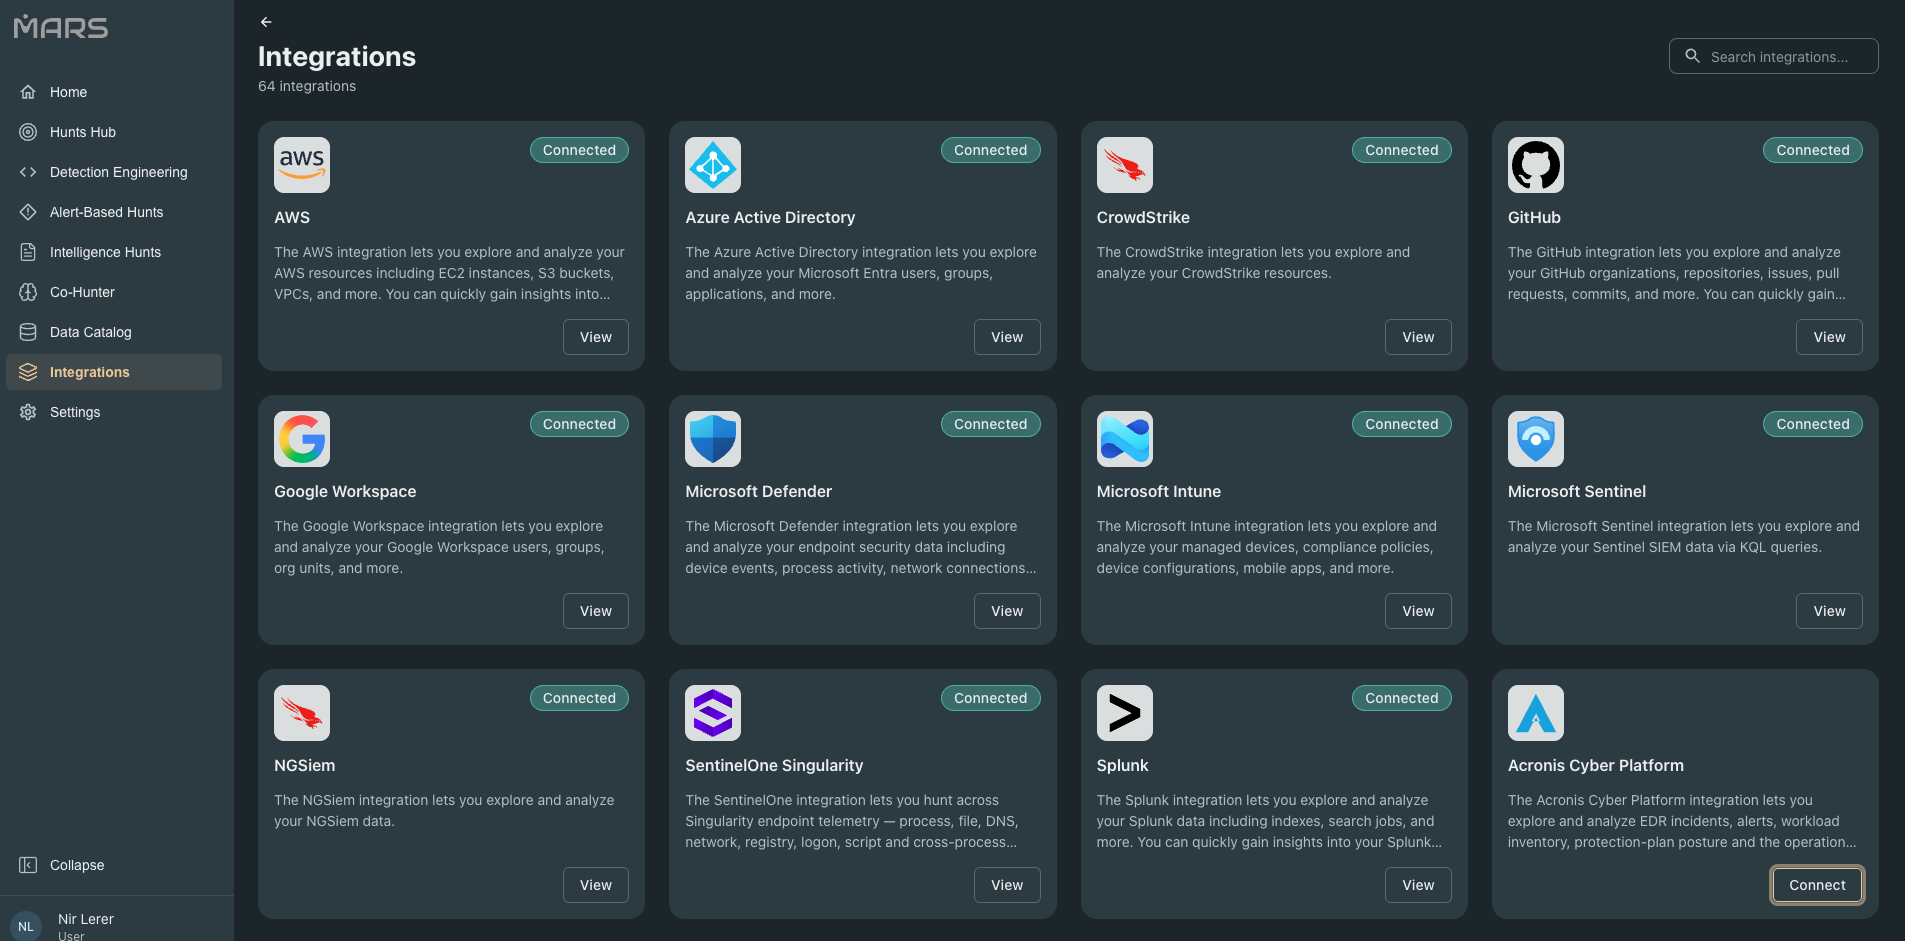
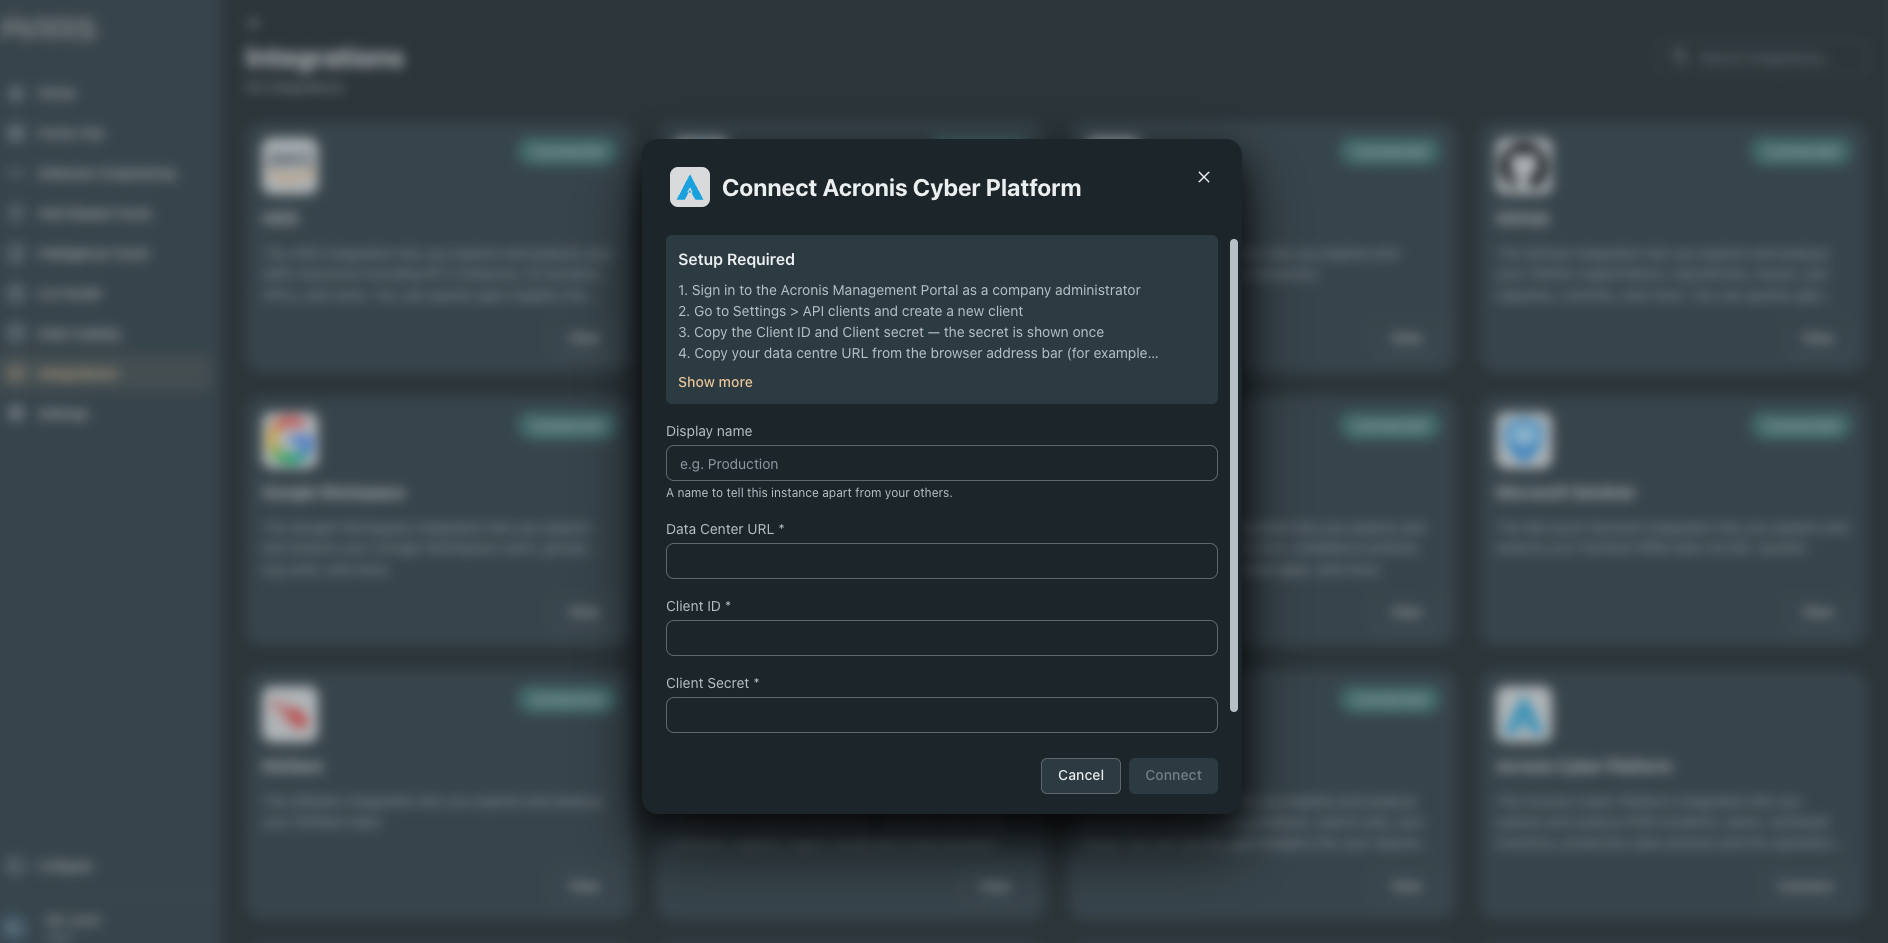
- The Acronis Cyber Platform integration lets you explore and analyze EDR incidents, alerts, workload inventory, protection-plan posture and the operational audit trail, plus raw endpoint sensor telemetry (process, network, registry, script, file and logon events) for Windows workloads. Acronis exposes raw telemetry for Windows only; macOS and Linux workloads contribute incidents, alerts and inventory. Mars also connects to dozens of integrations across SIEM, EDR, identity, cloud, email, vulnerability management and threat intel, including Splunk, Microsoft Sentinel, Google SecOps, CrowdStrike, SentinelOne, Microsoft Defender, Okta, Entra ID, AWS and Wiz. What teams get
- 15x more threat hunts than manual hunting
- 50+ relevant threat campaigns turned into hunts every week
- 4x expansion in MITRE ATT&CK detection coverage
- Up to 90% fewer false positives when hunt results become production detections
- A new threat campaign turned into a live hunt across your stack in under 3 hours
Explore resources
Mars Security + Acronis Cyber Platform in action
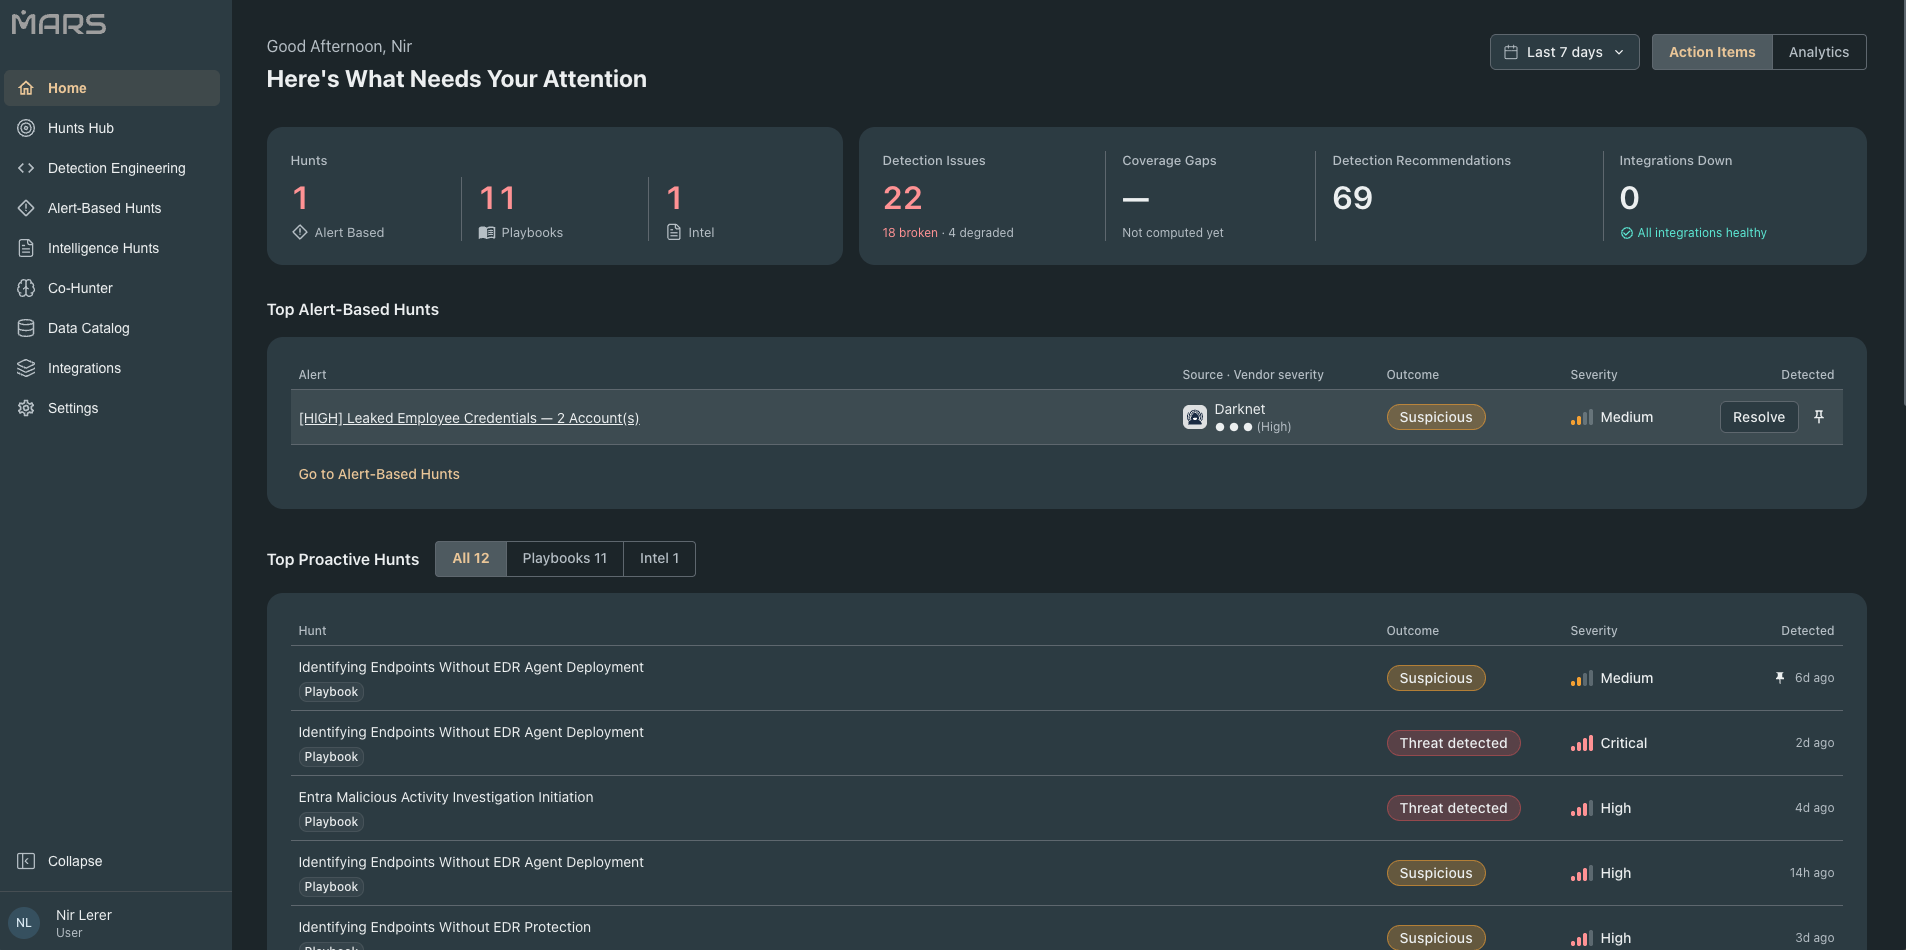
Features
Threat intel to detection in minutes
Mars reads threat intelligence continuously, extracts attacker TTPs, and deploys production-ready detection logic. The intel you already pay for stops sitting in reports.
Campaign-driven threat hunting
Hunts are built from real attacker campaigns and TTPs, not alert patterns. Built by founders who ran offensive operations, so Mars looks where attackers actually go.
Detections in your SIEM's native language
Mars translates, validates, and continuously tunes each detection for the SIEM you run. Work that takes days or weeks per rule runs in minutes.
Provable coverage
35+ threat campaigns mapped to your environment every month. Gaps found and closed, with full visibility into which attacks your stack would catch today.
No data ingestion
Mars connects by API to SIEM, EDR, identity, cloud, and data lakes. No data ingestion. No tool replacement. No additional headcount.