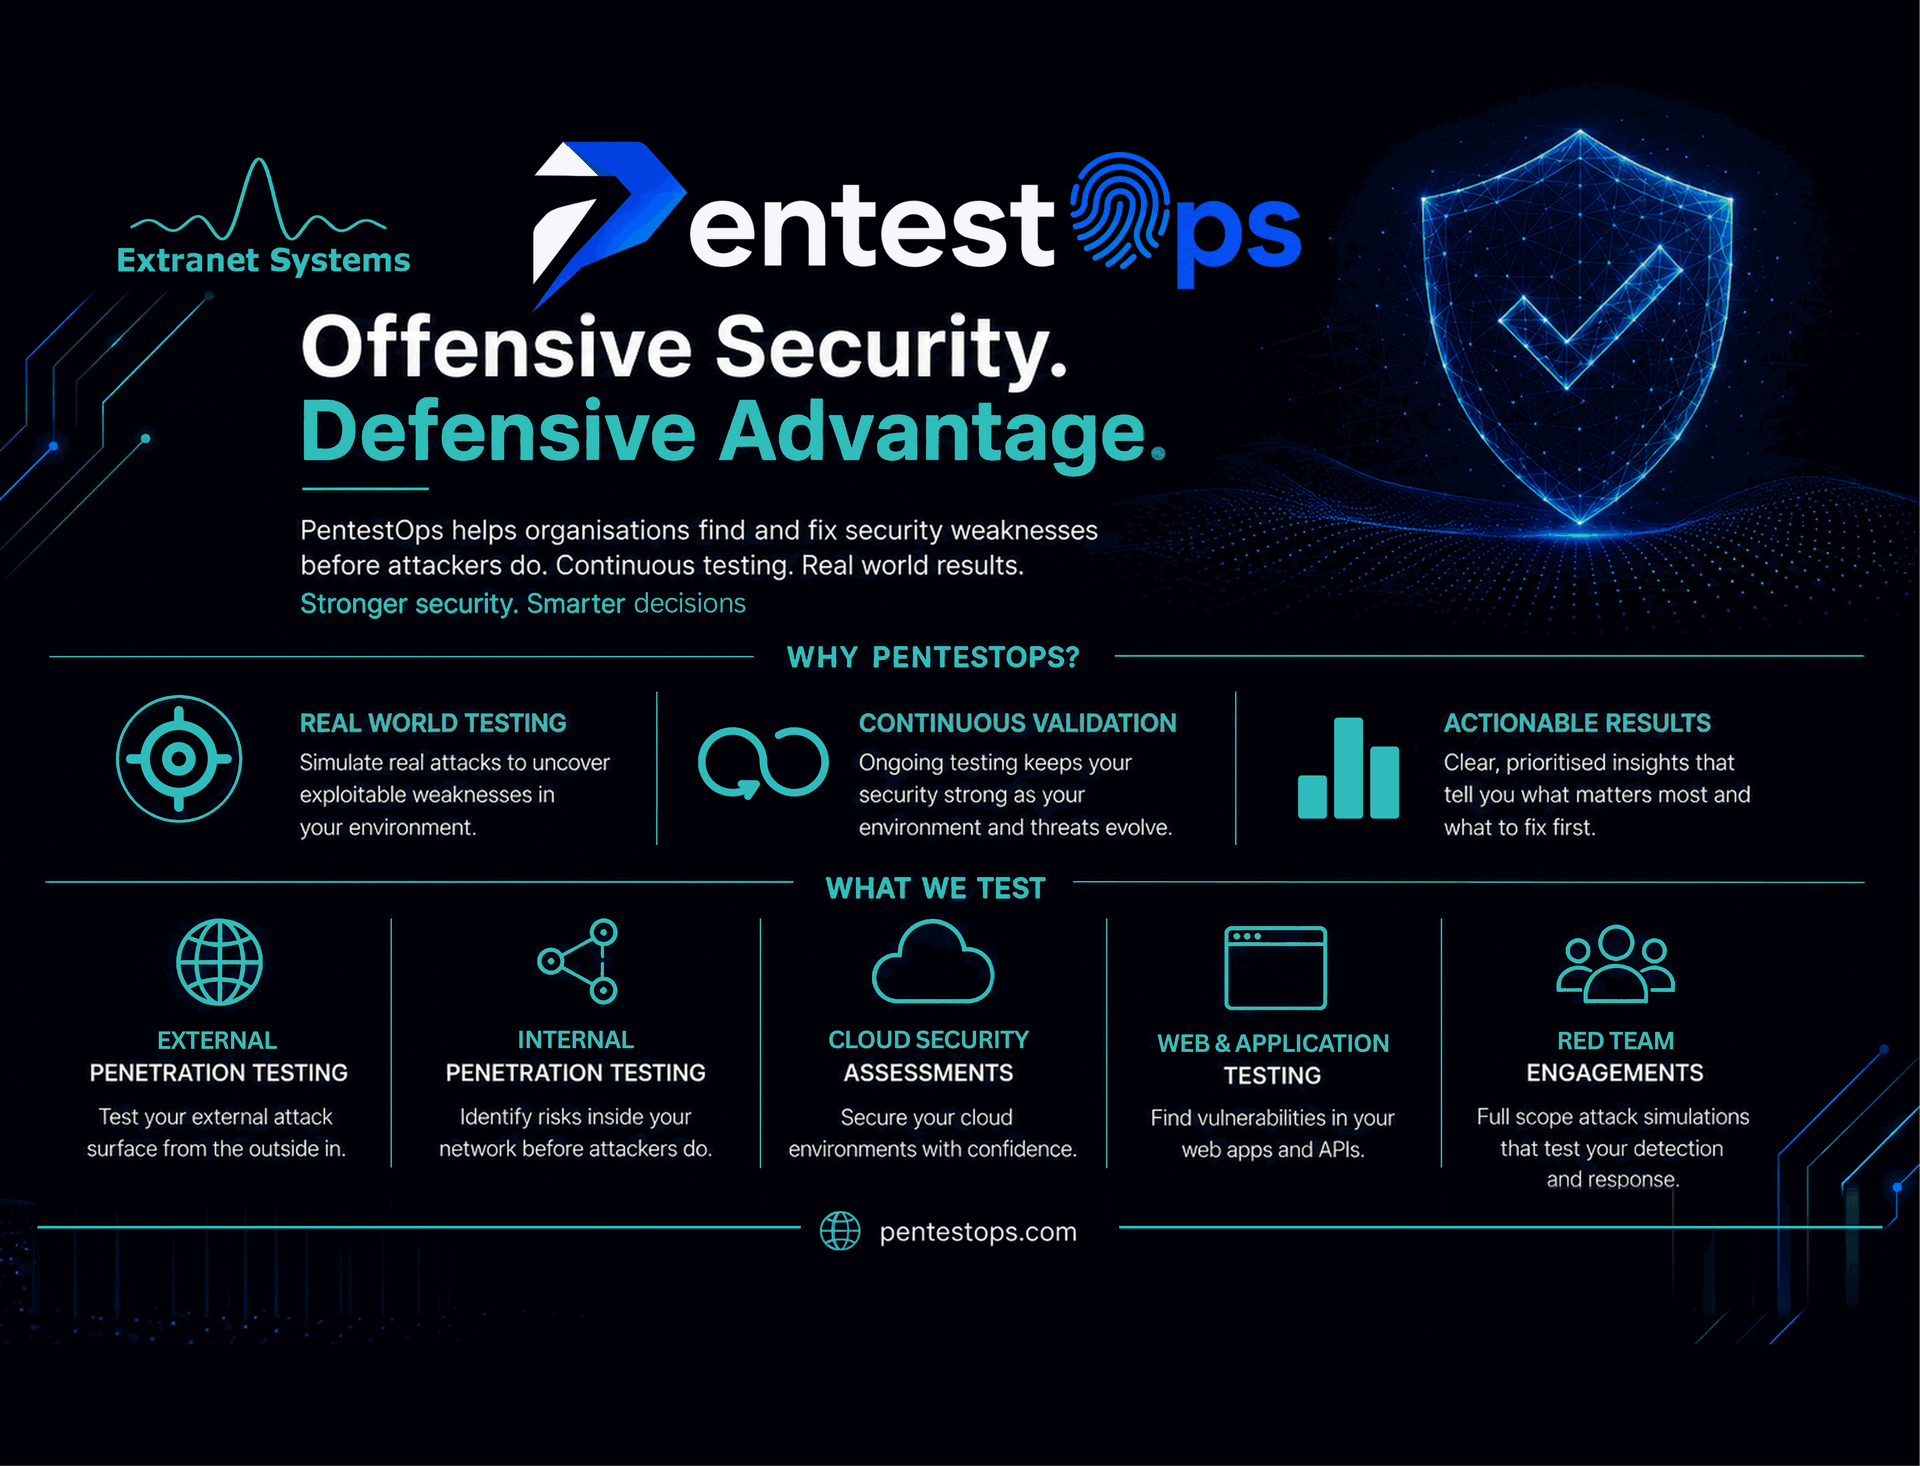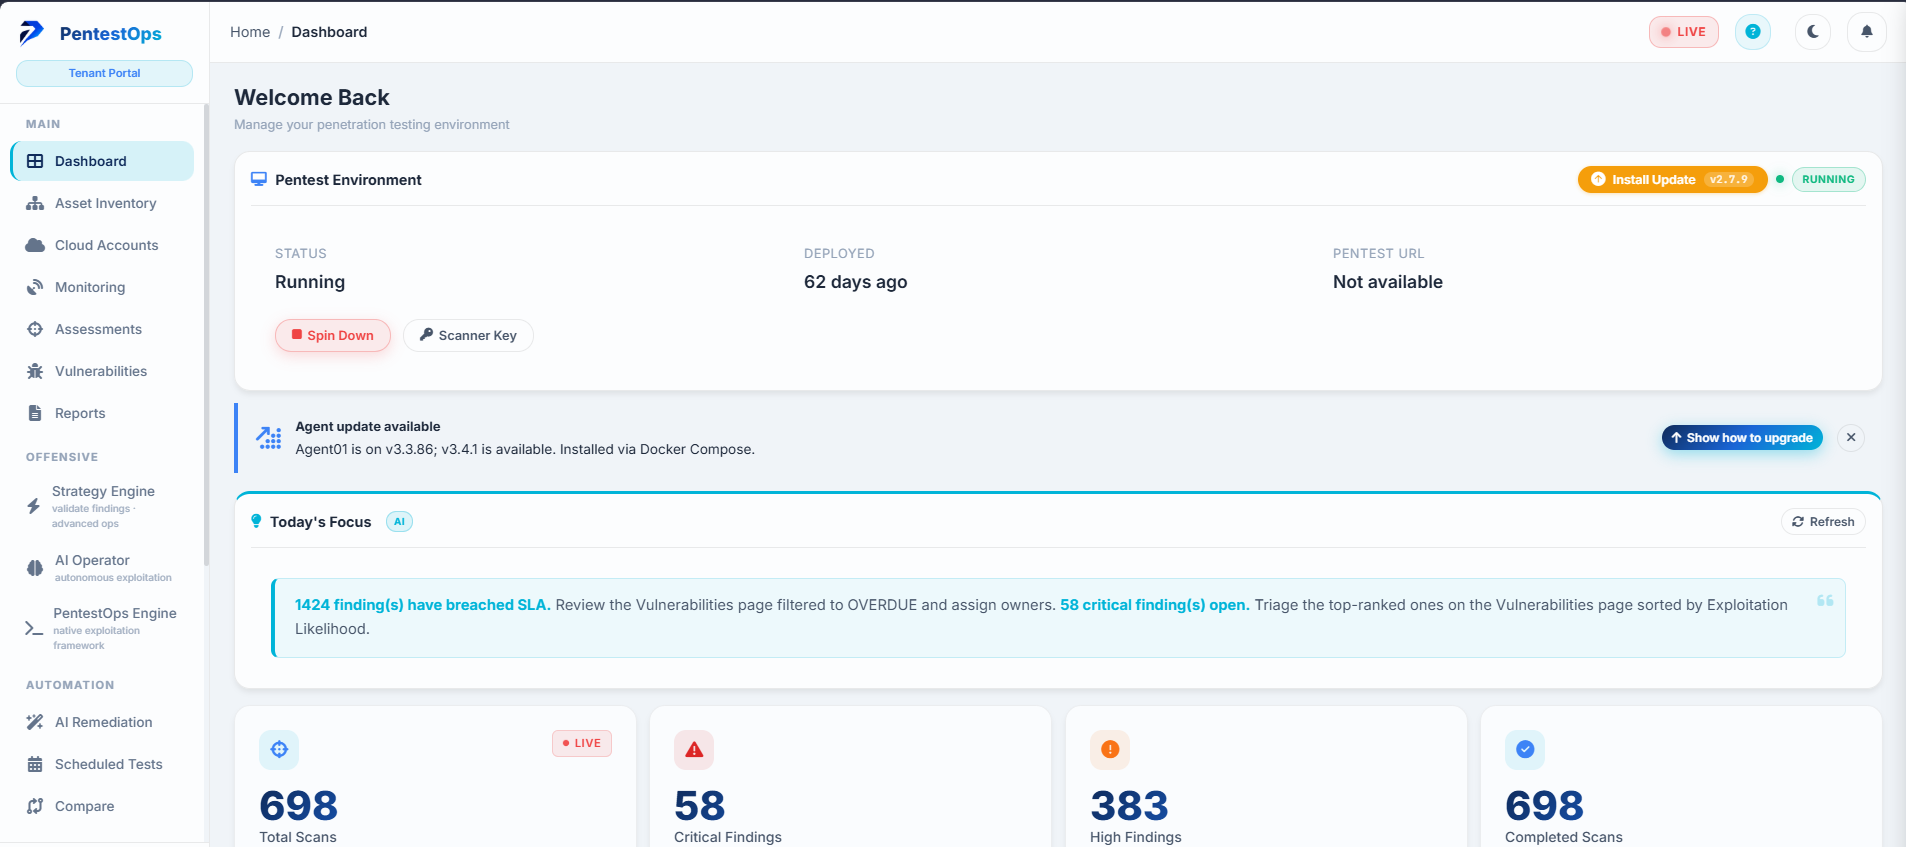

Traditional penetration testing happens once or twice a year, leaving organisations blind to new vulnerabilities introduced between assessments. PentestOps closes this gap by delivering continuous, automated security testing that thinks and acts like a skilled human pentester combining the speed and scale of AI with the depth and accuracy of manual testing techniques.
- Continuous discovery automatically maps your attack surface across cloud environments, web applications, APIs, networks, and internal systems as they change.
- Exploit validation goes beyond simple vulnerability scanning by actively validating whether weaknesses are truly exploitable, eliminating false positives and alert fatigue.
- Risk prioritization ranks findings by real-world exploitability and business impact, so security teams can focus on what matters most.
For MSPs and MSSPs, this also means the ability to deliver ongoing and scalable security testing across multiple client environments.