
Acronis integration with Splunk SIEM, facilitated by the Acronis SIEM Connector, enables the seamless transfer of vital Acronis Alerts and Audit Log data into the Splunk environment. This integration empowers organizations to gain deeper visibility into their Acronis ecosystem, enabling them to identify potential security risks and operational issues proactively. By centralizing Acronis data in Splunk, security analysts can leverage Splunk's powerful search and correlation capabilities to detect anomalies and threats. Furthermore, this integration allows for streamlined compliance reporting and improved incident response workflows, strengthening an organization's overall security posture.
Acronis Cyber Platform integration with Splunk Cloud Platform
Splunk Cloud Platform is a powerful security information and event management (SIEM) platform that enables organizations to collect, analyze, and correlate security data from various sources, providing real-time visibility and threat detection capabilities for effective incident response and proactive security management. The integration between Acronis Cyber Platform and Splunk SIEM helps MSPs automate threat detection across all customer networks and endpoints.
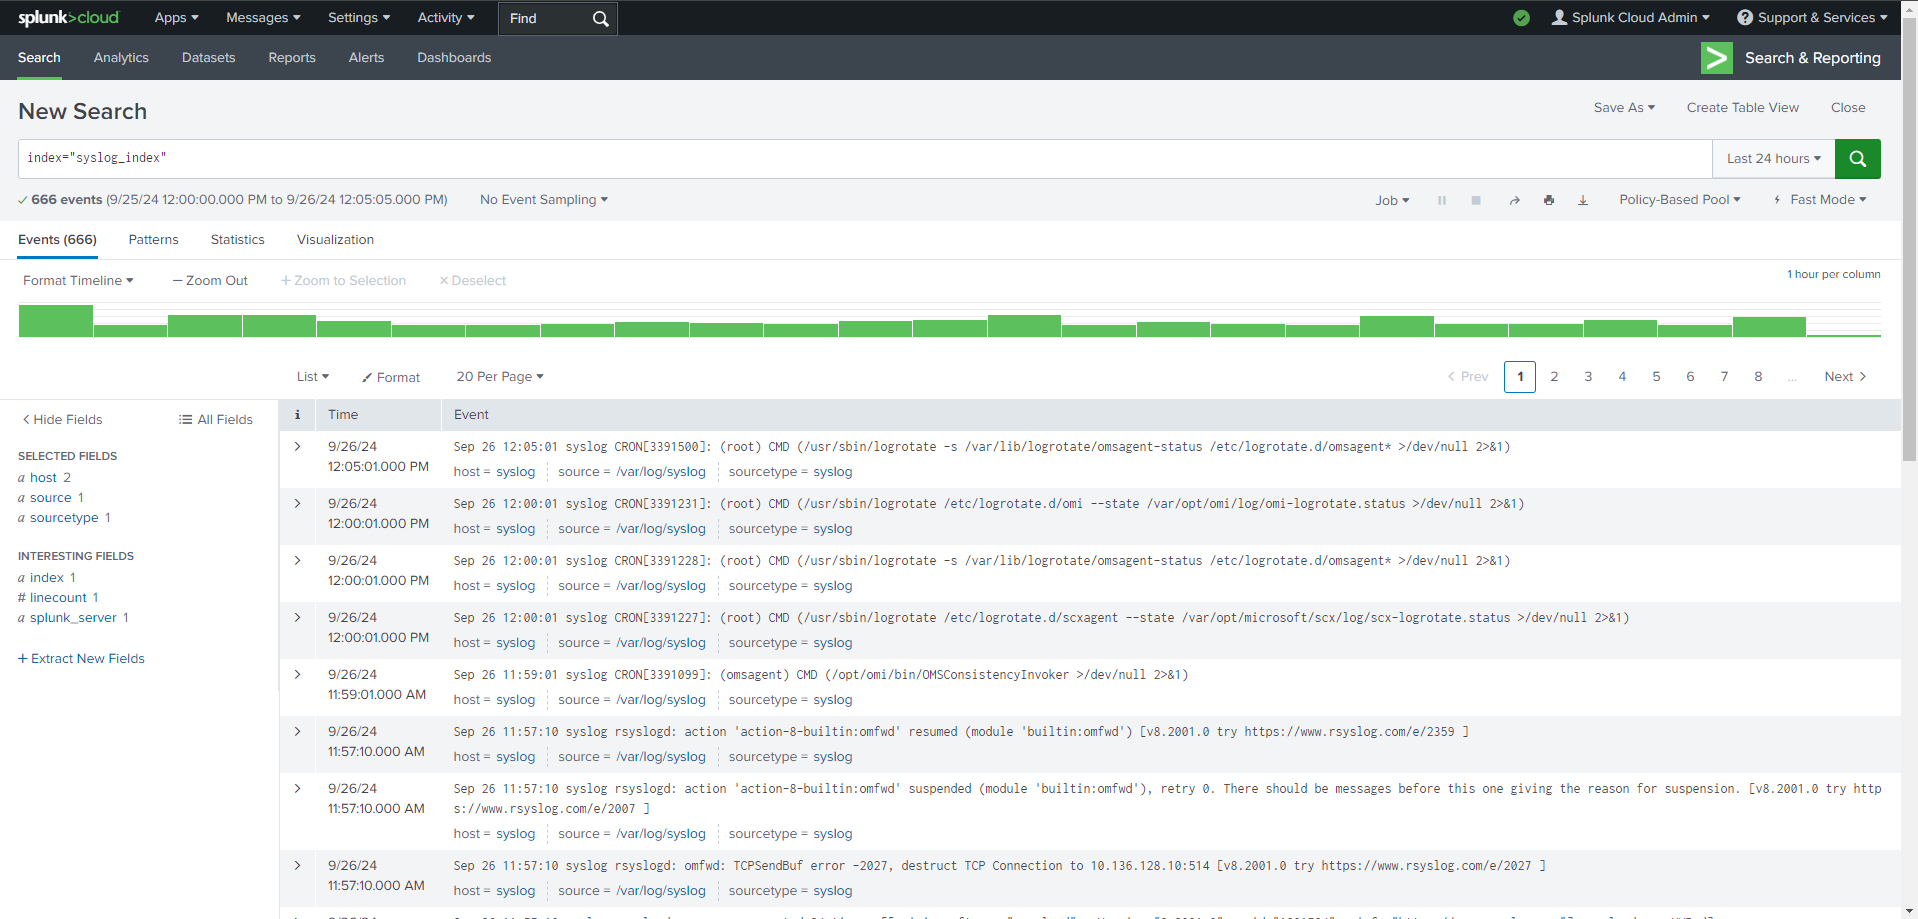
This integration is enabled through the Acronis SIEM Connector. The SIEM Connector uses the Acronis agent as a log writer, enabling MSPs to store Acronis Alerts, Events, Activities, and Audit Log on any endpoint in the customer network from where they can be ingested by the SIEM, or send those logs to a syslog server. The Connector supports CEF and JSON log formats.
Explore resources
Add Acronis to your Splunk Cloud Platform and centralize Incident Investigation
Features
Proactive Threat Detection and Response
By consolidating Acronis security data in Splunk, MSPs gain a comprehensive view of their clients' Acronis environments, enabling them to proactively identify and respond to potential threats before they impact their clients' data. This improves the MSP's ability to provide effective security services and protect their clients from cyberattacks.
Enhanced Client Reporting and Compliance
The integration enables MSPs to generate detailed security and compliance reports based on Acronis data for their clients. This provides clients with greater transparency into their security posture and helps MSPs demonstrate the value of their services.
Efficient Incident Management and Troubleshooting
Centralized access to Acronis alerts and audit logs in Splunk streamlines incident investigation and troubleshooting for MSPs. This allows for faster resolution of issues and minimizes client downtime, resulting in improved client satisfaction.
Have a Syslog Server? Integration setup is easy
Acronis supports core event format - CEF (Common Event Format), enabling MSPs to work with the data sent by the integration out of the box. Alerts are pre-formatted on Acronis side and don't require MSP to create any additional rules on SIEM side. Integration is setup only by providing server and client certificates