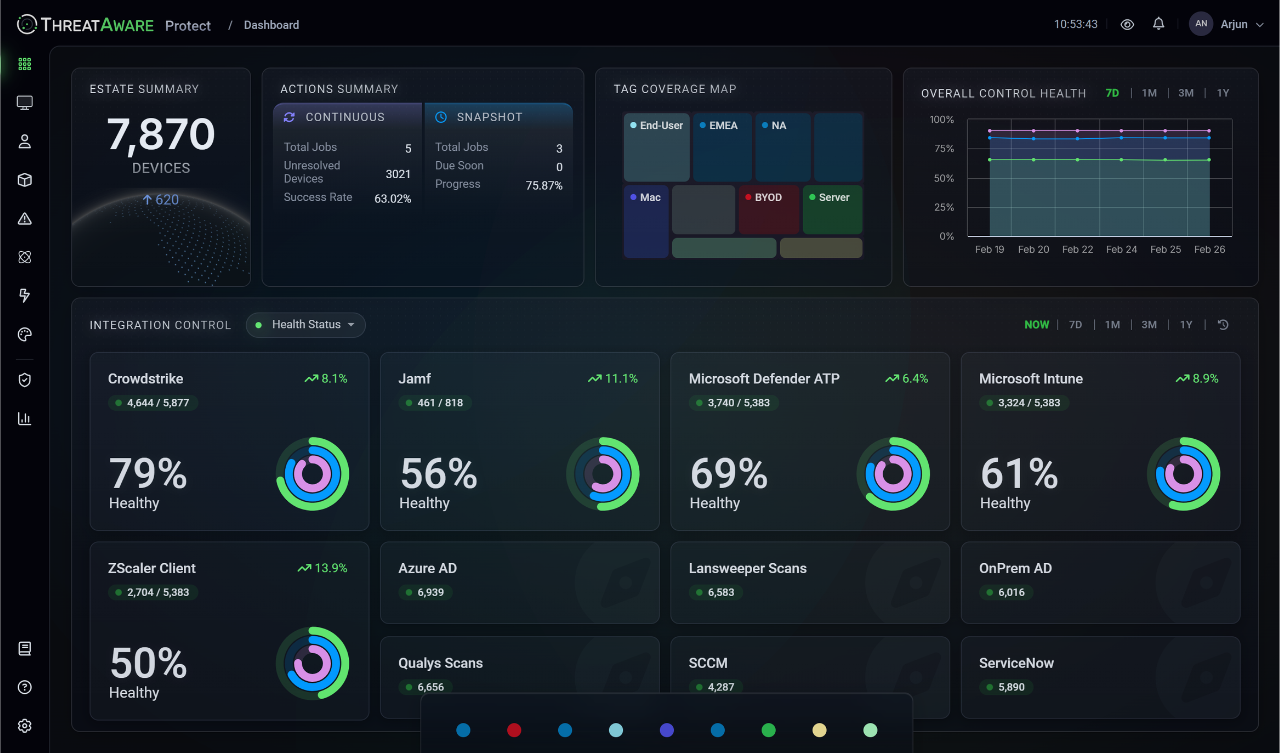
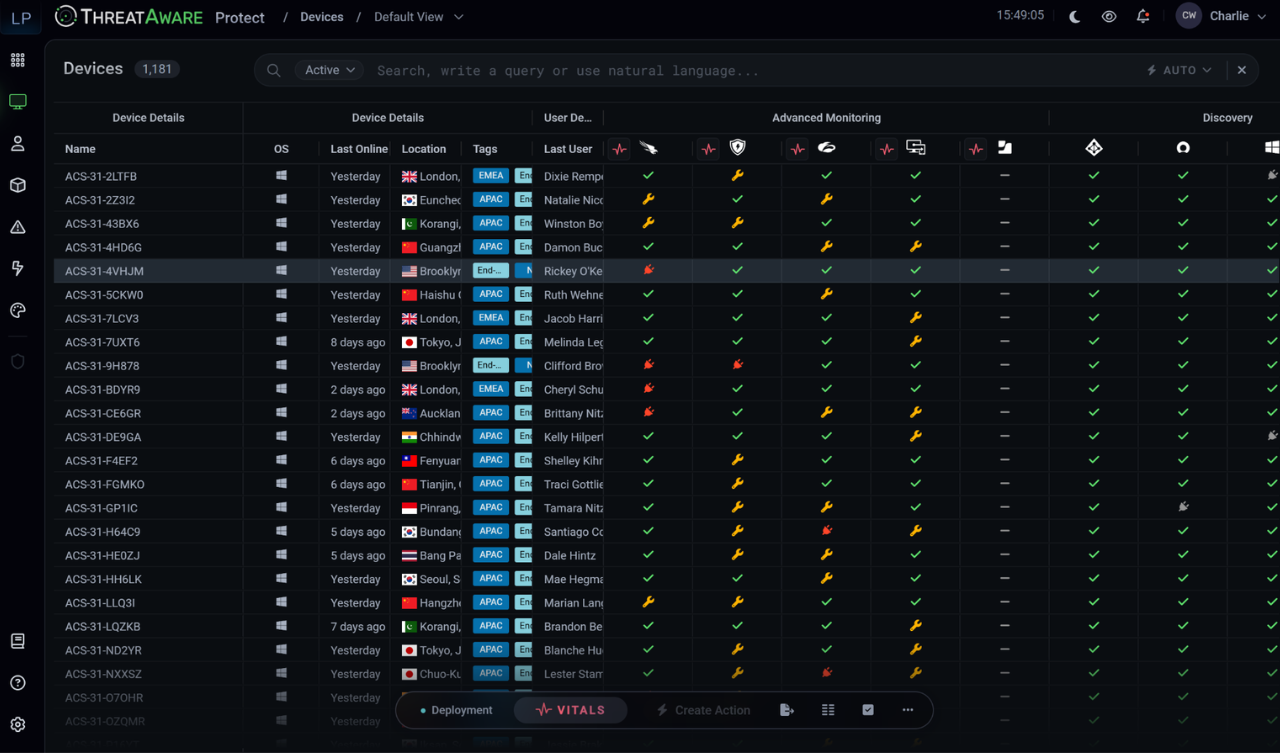
- ThreatAware connects agentlessly via secure, read only APIs to directories, MDM, EDR and SSO platforms, and can go fully live within an hour. Once connected, it runs continuous 60 minute vitals checks across every asset, flagging unknown devices that never appeared in any managed console, BYOD and personal devices bypassing corporate controls, silent agent failures and broken communication heartbeats, local policy drift and misconfigured controls, and coverage gaps where a mandated tool is meant to be running but isn't.
- ThreatAware combines identity layer stealth detection, reading authentication logs directly at the SSO and identity provider level to uncover hidden endpoint blind spots and BYOD devices, with independent cross stack validation that normalises telemetry from directories, MDMs and EDRs to confirm whether mandated security tools are actually deployed and active. Continuous vitals monitoring tracks asset health on a rolling 60 minute loop.
Acronis Cyber Platform integration with ThreatAware
The Acronis Cyber Platform and ThreatAware integration helps MSPs identify devices, users and endpoints that fall outside Acronis protection coverage. By continuously validating inventory data across identity, endpoint and management platforms, ThreatAware helps service providers find missing Acronis agents, silent agent failures and unmanaged devices before they create backup or security gaps. ThreatAware is the agentless layer that gives full visibility of every device across an estate, closing the gaps that sit outside Acronis backup and endpoint coverage. Most enterprises run cyber hygiene at somewhere between 70% and 80%, not because their tools are failing but because asset growth, remote work and BYOD access have outpaced what any single console can see. Backup and endpoint tools protect what they know about. The devices they don't know about are the ones that end up unprotected, unbacked up and undiscovered until something goes wrong. ThreatAware integration with Acronis closes that gap. Rather than relying on network layer scanning or fragile metadata matching, which can misidentify devices or miss them entirely, ThreatAware uses patented Timeline Matching, aligning behavioural timelines from multiple sources to deliver over 99% trusted asset visibility with empirical proof, not a best guess.
How ThreatAware works with Acronis
Use cases
Visibility of missing Acronis agents
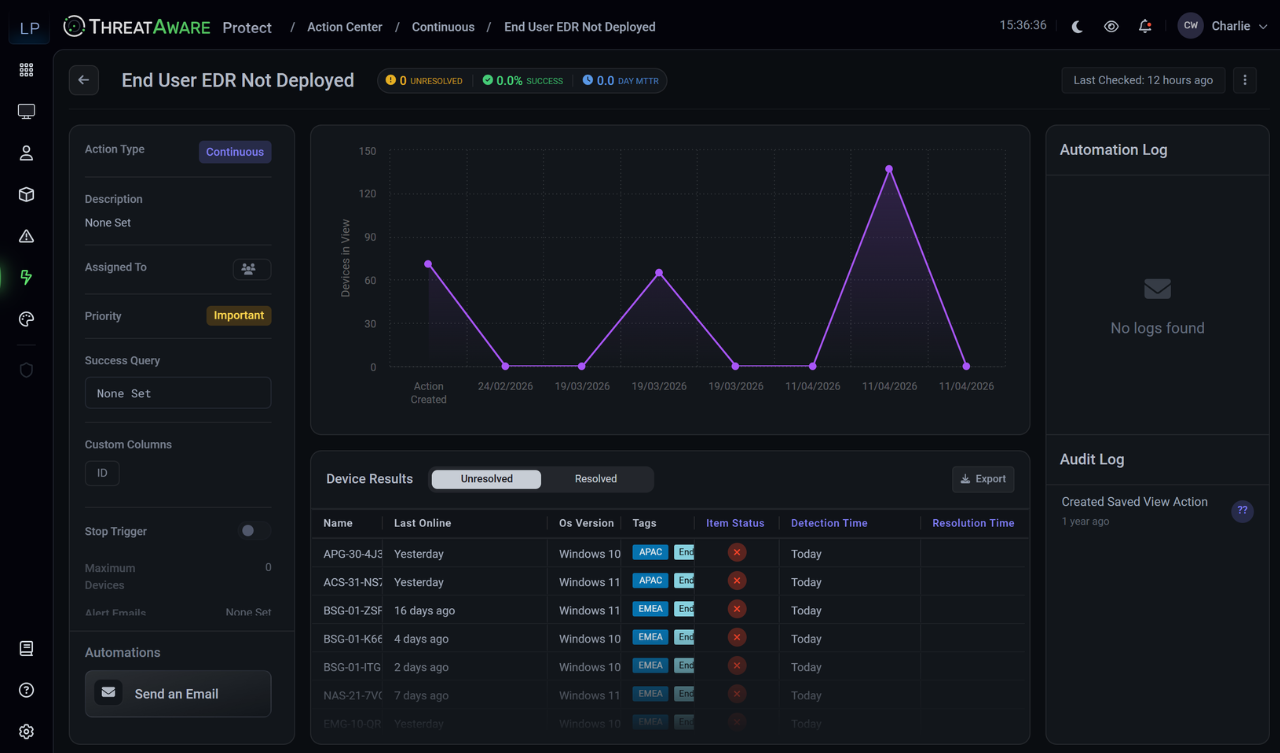
Flags every device across an estate where the Acronis agent isn't installed, so gaps in backup and endpoint coverage are visible before they cause a failed recovery, not discovered after one. Rather than relying on the Acronis console alone, which can only report on what it already knows about, ThreatAware cross references device data from directories, MDM, EDR and SSO sources to build an independent picture of the full estate, then highlights exactly where Acronis coverage stops.
Detection of silent agent failures
Runs a continuous 60 minute vitals check on every device, catching Acronis agents that have crashed, stopped reporting or drifted out of policy, even when the console still shows a device as protected based on the last successful check in. Silent failures are one of the most common causes of backup gaps, because a dashboard built on historical data has no way of showing a problem that happened after the last report came in.
Discovery of unknown and BYOD devices
Reads authentication logs directly at the identity and SSO layer to surface devices that never had an Acronis agent deployed at all, including personal and BYOD devices that bypass standard rollout processes entirely. This closes a blind spot no backup or endpoint platform can see on its own, since it can only report on devices it has already been installed on.
Single hygiene view across every client
Gives MSPs one continuous, live picture of Acronis agent coverage across their full client base, replacing manual, tenant by tenant checks with a single dashboard. Instead of reviewing each client's Acronis console separately to confirm coverage, MSPs get one place to see every gap across every tenant, updated continuously rather than at the point of a manual audit.