What is malware?
Malware, short for malicious software, is a broad term covering any program or code intentionally designed to harm, exploit, or compromise a computer system, network, or user. The category includes ransomware, trojans, worms, spyware, infostealers, and many other families, each with distinct behaviors and objectives. Malware can steal sensitive data, encrypt files for ransom, destroy information, hijack system resources, or provide attackers with persistent remote access.
The growing diversity of malware and the speed at which new variants appear make it a foundational threat to every digital environment. SonicWall detected 6.06 billion malware attacks globally in 2023, a 10% increase over the prior year (SonicWall 2024 Cyber Threat Report, via Statista). At the same time, adversaries are moving away from traditional malware binaries. In 2025, 82% of detections observed by CrowdStrike were malware-free, with attackers using valid credentials and hands-on-keyboard techniques to blend in with legitimate activity (CrowdStrike 2026 Global Threat Report).
Why it matters: the business impact of malware
A successful malware infection is not a minor inconvenience. It is a significant business risk that can lead to:
Financial loss. Direct costs include ransom demands, regulatory fines, and forensic investigation. Indirect costs include business interruption, lost revenue, and increased insurance premiums. The average cost of a data breach in 2025 was $4.44 million globally and $10.22 million in the United States (IBM Cost of a Data Breach Report 2025).
Data theft and exposure. Attackers steal intellectual property, customer records, payment data, and trade secrets. This theft can trigger compliance fines under frameworks such as GDPR and HIPAA, class-action lawsuits, and long-term competitive harm.
Operational downtime. Malware can disable critical servers, shut down production lines, or destroy backups, causing prolonged outages. Recovery efforts typically extend beyond 100 days for organizations that experience a breach (IBM 2025).
Reputational damage. A public breach erodes customer trust and investor confidence, causing long-term harm to the brand that outlasts the technical recovery.
Anatomy of an attack: how malware typically operates
While different malware families behave in unique ways, most follow a similar pattern once they reach a device or network.
Delivery. Attackers deliver malware through phishing emails, malicious downloads, compromised websites, drive-by exploits, supply-chain compromise, or exploitation of unpatched vulnerabilities. Phishing remains the single most common initial access vector for malware and ransomware (Verizon 2025 DBIR).
Execution and persistence. Once activated, the malware runs on the system, attempts to bypass security controls, and may establish persistence so it survives reboots or user intervention. Techniques include scheduled tasks, registry modifications, and DLL side-loading.
Spread. Many strains attempt to expand their reach by moving laterally across the network, harvesting credentials, or probing for additional vulnerable systems.
Impact. Finally, the malware carries out its objective: encrypting data, exfiltrating information, spying on user activity, destroying files, or enabling persistent remote access.
Attacker’s toolkit: common malware types
Malware is a broad category covering several distinct families. The table below describes the major types encountered in modern threat environments.
AI-generated malware and malware-as-a-service
Malware-as-a-service (MaaS) is a commercial model in which malware developers sell or lease ready-made toolkits to affiliates who carry out attacks. According to the Darktrace 2024 Annual Threat Report, MaaS accounted for 57% of all cyber threats detected in the second half of 2024, a 17-percentage-point increase from the first half. Recorded Future’s 2024 Malicious Infrastructure Report found that MaaS infostealers led by LummaC2 were the dominant infection type, with 384 unique malware varieties sold across the top three criminal forums. Threat actors are also using generative AI to craft more convincing phishing lures and accelerate development cycles. The CrowdStrike 2026 Global Threat Report documented an 89% increase in attacks by AI-enabled adversaries compared to 2024.
Warning signs: how to tell if you have malware
A malware infection does not always announce itself immediately. Recognizing early indicators helps reduce dwell time and limit damage.
System performance and stability. Unexplained slowdowns, frequent crashes, application freezes, or persistent overheating during periods of low user activity may indicate a background process consuming system resources. Sustained high CPU or GPU usage with no obvious user-initiated cause is a common sign of cryptojacking.
Unauthorized changes. New programs, browser extensions, or toolbars appearing without user action suggest adware or trojan activity. Changes to browser homepages, default search engines, or DNS settings point to browser hijacking. Unexpected new user accounts with elevated privileges may indicate lateral movement.
Network anomalies. Unusual outbound traffic, connections to unfamiliar external IP addresses, or high data transfer volumes during off-hours can signal data exfiltration or C2 communication.
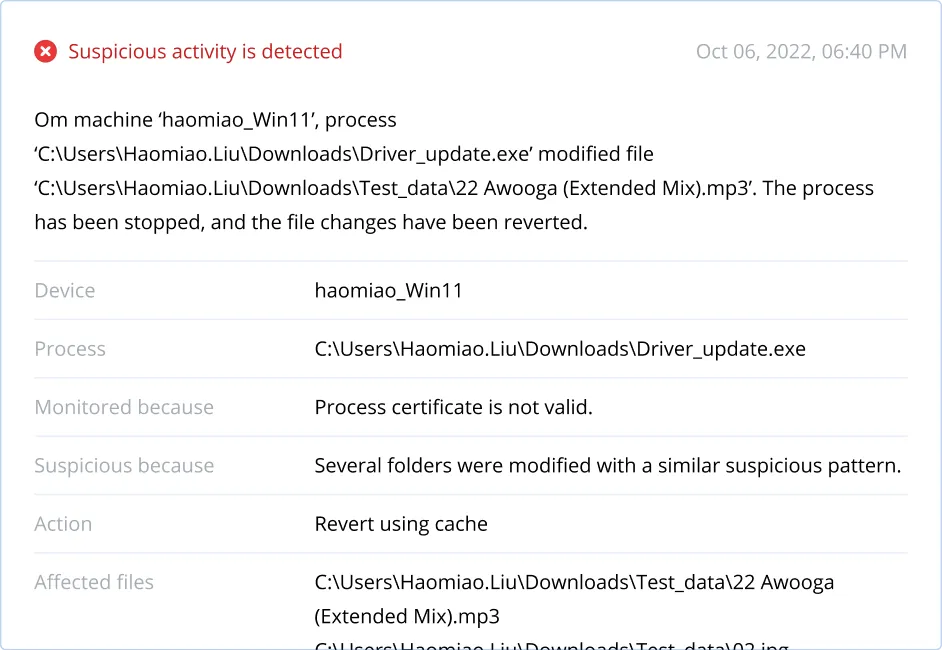
Ransomware-specific indicators. Rapid, sequential file modifications across multiple directories, deletion or disabling of volume shadow copies, and the appearance of ransom notes or files with unfamiliar extensions.
Credential and account anomalies. Unexpected account lockouts, password reset notifications the user did not initiate, or logins from unfamiliar geographic locations may indicate infostealer activity or credential compromise.
Endpoint security interference. Disabled antivirus or EDR agents, missing security updates, or errors when launching security tools can indicate malware is actively suppressing defenses.
If any combination of these signs is present, isolate the affected endpoint from the network and initiate incident response procedures before attempting remediation.
Stopping the attack: detection and incident response
Malware evolves too quickly for signature-based tools to keep pace. Effective defense relies on behavioral detection and disciplined incident response.
Modern detection
Watch for anomalous behavior. Early signs include unauthorized PowerShell commands, rapid file modifications, unexpected RDP logins, and deletion of volume shadow copies. These indicators often surface before encryption or exfiltration begins.
Cross-signal monitoring. Correlate events across endpoints, logs, and the network. Windows event logs and Sysmon parent-child process chains can flag suspicious process spawning, while firewall logs reveal outbound connections to unusual IPs.
Malware using legitimate services. Recent campaigns have abused compromised VPN and Active Directory credentials and used WMI to deploy backdoors. Once installed, attackers use collaboration platform APIs to establish C2 channels. Detecting these threats requires monitoring for unexpected network traffic to collaboration platforms and side-loaded DLLs.
Why real-world examples matter
Destructive malware. Wiper families such as WhisperGate, FoxBlade, and CaddyWiper have been used in geopolitical operations to overwrite system files and boot records. Wipers permanently destroy data and can render recovery impossible. Preparation requires robust, immutable backups and a clear recovery plan.
Adaptive backdoors. Backdoors delivered via unpatched vulnerabilities embed configuration files that appear innocuous. These stealth techniques highlight the need for continuous patch management and behavioral analytics.
Effective response
Isolate and contain. Immediately disconnect infected endpoints or segments to prevent lateral movement and preserve forensic evidence.
Investigate root cause. Determine how the malware entered (phishing, exploited vulnerability, stolen credentials) and close that entry point.
Restore from clean backups. Verify the integrity of backups before restoring. Wipers and ransomware can corrupt backups that are not protected by immutability and air gapping.
Remediate and harden. Apply patches, reset compromised credentials, and strengthen controls (enforce MFA, remove unused services, review access policies).
How to remove malware
If malware is detected on a system, follow a structured removal process to avoid reinfection or further damage.
1. Disconnect the device from the network to prevent lateral movement, data exfiltration, or communication with C2 servers. For ransomware, this step is critical to stop encryption from spreading to file shares.
2. Boot into safe mode or use a recovery environment to prevent the malware from running during cleanup. On Windows, safe mode with networking allows downloading updated security tools if needed.
3. Run a full scan with updated anti-malware software. Use a reputable endpoint protection tool with current definitions. If the existing tool was compromised, use an offline or bootable scanner.
4. Remove detected threats and quarantine suspicious files. Follow the tool’s remediation guidance. For rootkits or persistent threats, a full OS reinstallation from a known-clean image may be required.
5. Restore data from verified backups. Scan backup images with the latest anti-malware definitions before restoring to avoid reintroducing the infection.
6. Reset credentials and patch the entry point. Change all passwords that may have been exposed, revoke active sessions, enable MFA, and apply any missing security patches.
For enterprise environments, engage your incident response team or a managed detection and response (MDR) provider. Document the attack for post-incident review and compliance reporting.
Proactive defense: prevention strategies and best practices
Organizations can significantly reduce malware incidents by adopting a layered security (or defense-in-depth) strategy.
Technical controls. Deploy modern anti-malware solutions with behavioral detection. Enforce strict software patching and vulnerability management. Use multifactor authentication (MFA) everywhere.
Network security. Use network segmentation to prevent lateral movement. Monitor traffic for anomalies and block connections to known-malicious infrastructure.
User training. Conduct regular security awareness training to help employees spot phishing and social engineering. Organizations with regular training see significantly lower phishing click rates.
Data protection. Maintain regular, automated, and tested backups with offline or immutable copies. This is critical for recovering from ransomware and wiper attacks.
Endpoint visibility. Deploy EDR or XDR for real-time visibility into endpoint activity and rapid threat containment. Application allowlisting helps restrict unauthorized software execution.
Layered defense: How Acronis protects you
Defending against modern malware requires multiple, integrated layers. Acronis Cyber Platform (formerly Acronis Cyber Protect Cloud) integrates AI-powered cybersecurity and data protection to stop threats:
• Behavioral detection: Monitors system processes in real-time and stops zero-day malware by identifying suspicious behavior before it can execute and cause damage.
• Active anti-malware: Performs continuous scanning and memory inspection to block known and emerging malware threats, including viruses, trojans and infostealers.
• Ransomware rollback and recovery: For ransomware attacks, Acronis enables one-click restoration of affected files from immutable backups, neutralizing encryption attacks and rendering them ineffective.
Connecting the Dots: Related Attacks & Insights
Malware FAQ: Executive strategy and organizational risk
What economic and operational impacts can a malware or data extortion incident cause?
How fast and sophisticated are modern malware campaigns?
Should an organization ever consider paying an extortion demand?
What is the most important technical safeguard for fast recovery from malware?
Malware FAQ: Prevention and security architecture
How can we implement access controls that limit malware spread inside the network?
What security controls are recommended for RDP and VPN services?
How should organizations manage risk from internet-facing vulnerabilities?
How can we defend against fileless malware and precursor infections?
What steps help prevent malware delivered through email?
How does managing third-party and MSP access reduce malware risk?
Malware FAQ: Detection, analysis and incident response
What are the first steps teams should take when malware is detected?
How can centralized logging improve malware detection and response?
What signs of compromise should threat hunters prioritize?
What does effective eradication and recovery look like after containing a malware incident?