There is no shortage of guidance available to MSPs on how they should secure customer environments. Security frameworks, industry standards, regulatory requirements and insurance obligations all provide recommendations on the controls organizations should have in place. Yet despite this abundance of guidance, cyber incidents remain common and continue to increase.
At the same time, requirements are becoming more complex. Frameworks such as NIST CSF and regulations like NIS 2 introduce additional expectations, while customers, auditors and insurers increasingly require proof that controls are not only implemented but remain effective over time.
The challenge is growing. Threat actors are executing attacks quicker and increasingly relying on large language models (LLMs) as a strategic force multiplier, according to Google Mandiant’s M-Trends 2026 Report. Research from Anthropic also shows that artificial intelligence can accelerate the exploitation of vulnerabilities, increasing both the speed and scope of cyber threats facing organizations today.
In this environment, security can no longer be treated as a set and forget exercise. MSPs need a new approach that continuously measures and improves security across customer environments.
Point assessments are no longer enough
Traditional compliance and security assessments provide a useful snapshot in time, but today's threat landscape requires something more dynamic. What organizations need is a live, operational approach that continuously measures security controls across the entire IT environment. Deviations should be visible immediately, remediation should be tracked and evidence should remain current.
Continuous compliance is not simply a reporting exercise. It becomes the evidence layer that supports real cyber resilience. MSPs need visibility into which framework requirements are impacted by each control, which technical measures support them, when evidence was last refreshed, whether exceptions exist, who owns each control and what remediation activity has taken place.
Posture management must continuously feed into the measurement and implementation of security controls to enable a near real-time view of compliance status and security posture.
Introducing Acronis Cyber Compliance
To meet this challenge, Acronis is introducing Cyber Compliance as part of Acronis Cyber Platform (formerly Acronis Cyber Protect Cloud).
Cyber Compliance helps MSPs deploy, measure and continuously monitor security controls across customer environments. Rather than treating compliance as a point-in-time audit exercise, Cyber Compliance enables a continuous compliance approach where evidence remains current and security controls are continuously assessed.
Compliance should not be viewed as an isolated certification activity. Instead, it must become an ongoing evidence layer that supports stronger cybersecurity outcomes and improved cyber resilience. Cyber Compliance helps MSPs continuously demonstrate which controls are implemented, where gaps exist and what remediation actions are needed.
By translating platform telemetry into control evidence, Cyber Compliance bridges the gap between security recommendations and operational execution. It helps MSPs focus on implementing and monitoring safeguards that meaningfully reduce customer risk.
First release capability: Built on proven security best practices
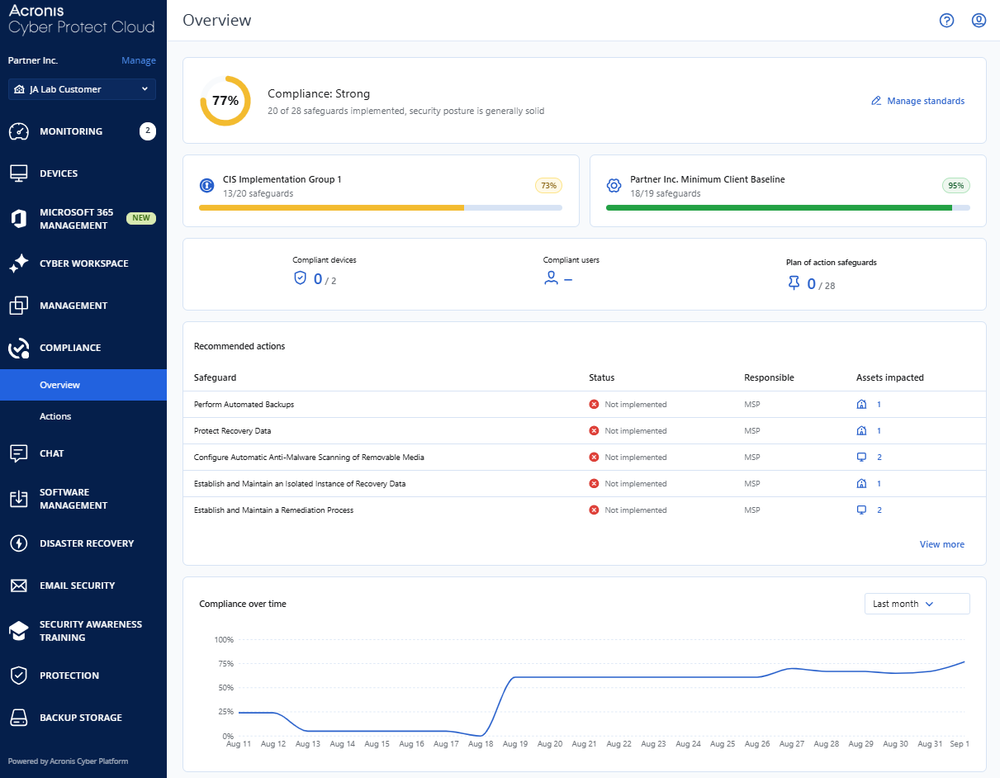
The first release of Cyber Compliance is built around the Center for Internet Security (CIS) Controls one of the world's most widely recognized cybersecurity best-practice frameworks. CIS Controls are comprised of safeguards that provide the foundation for measuring security posture and monitoring implementation progress.
With Cyber Compliance, MSPs can:
- Assess customer environments against CIS safeguards.
- Identify implemented, partially implemented and missing safeguards.
- Set ownership for individual safeguards (MSP or Customer).
- Monitor compliance status across all customers.
- Execute actionable recommendations to improve safeguard implementation.
- Measure and track progress over time.
- Create custom standards tailored to customer requirements.
The result is a practical approach to turning security best practices into measurable security outcomes.
Benefits today for MSPs
Cyber Compliance provides MSPs with a strong foundation for expanding beyond simple security monitoring. By bringing together live telemetry, remediation activities and visibility within a single platform, MSPs can create new opportunities to demonstrate value and strengthen customer relationships.
Designed for where MSPs are going next
The first release of Cyber Compliance is just the beginning.
Future enhancements will extend coverage beyond CIS Controls into popular compliance frameworks and standards, ISV ecosystem integrations, evidence preparation capabilities, exception management workflows, audit preparation features, AI-assisted remediation and more.
As compliance requirements continue to evolve, Cyber Compliance is designed to evolve alongside them, helping MSPs deliver scalable security, compliance and CISO services from a single platform.
Getting started
Cyber Compliance is available today for free within Acronis Cyber Platform. MSPs can start using the solution immediately to measure security controls and drive continuous security improvement across customer environments.
Keep calm and implement security controls, Cyber Compliance gives MSPs a structured way to do exactly that.
Product feedback? The Cyber Compliance product team would love to hear from you at [email protected].
Written by
About Acronis
Acronis is a leader in AI-native cyber protection, unifying data protection, cybersecurity, IT operations and hybrid infrastructure to deliver business continuity, security and compliance with less cost and complexity. More than 21,000 service providers trust Acronis to protect over 750,000 businesses in 150 countries. Acronis is headquartered in Schaffhausen, Switzerland.