Acronis GenAI Protection
Generative AI security for MSPs
Generative AI security is now a core concern for MSPs. As GenAI use spreads, it creates new AI security risks such as shadow AI, sensitive data exposure and AI data leakage, all with little visibility into how tools are used. Acronis helps MSPs and businesses secure generative AI by protecting sensitive data, controlling AI activity and managing risk across every workflow.
Top generative AI security risks organizations must address
As generative AI adoption grows, organizations face three core threats.
Shadow AI
Unapproved or unmanaged AI tool usage can create blind spots for MSPs and organizations, making it harder to monitor activity, enforce policies and maintain visibility across environments.
AI abuse
Malicious or manipulated prompts can influence AI behavior, leading to unsafe outputs, unauthorized actions or responses that bypass intended controls.
Data leakage and loss
Sensitive, regulated or confidential information can be exposed through AI interactions, retained outside approved boundaries or used in ways that increase compliance and security risk.
Best practices for secure AI adoption
Maintaining protection in AI environments requires a structured approach.
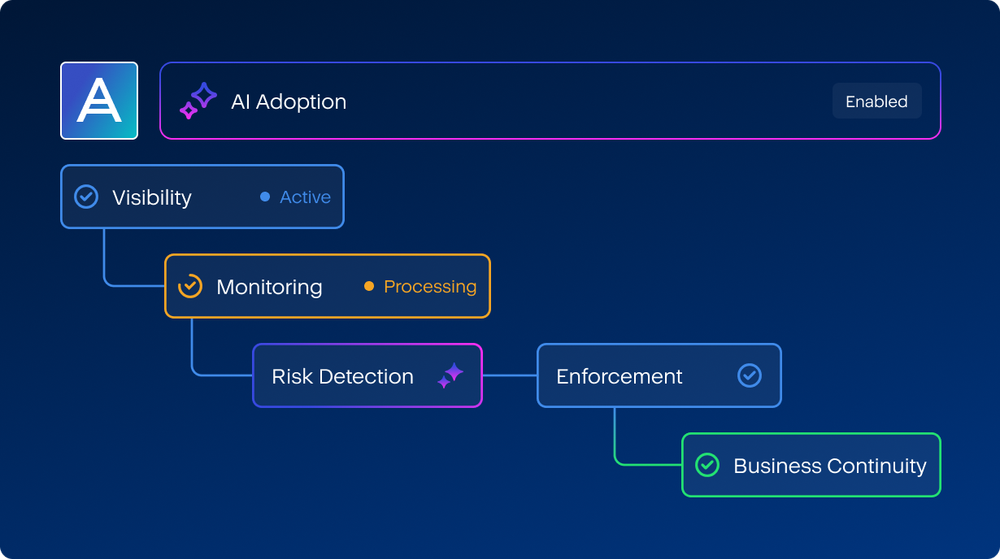
Visibility and discovery
Understand where AI is used and how it interacts with IT infrastructure and data.
Sensitive data protection
Inspect prompts for sensitive data and prevent unauthorized transfers.
Monitoring
Continuously observe usage and respond to potential issues.
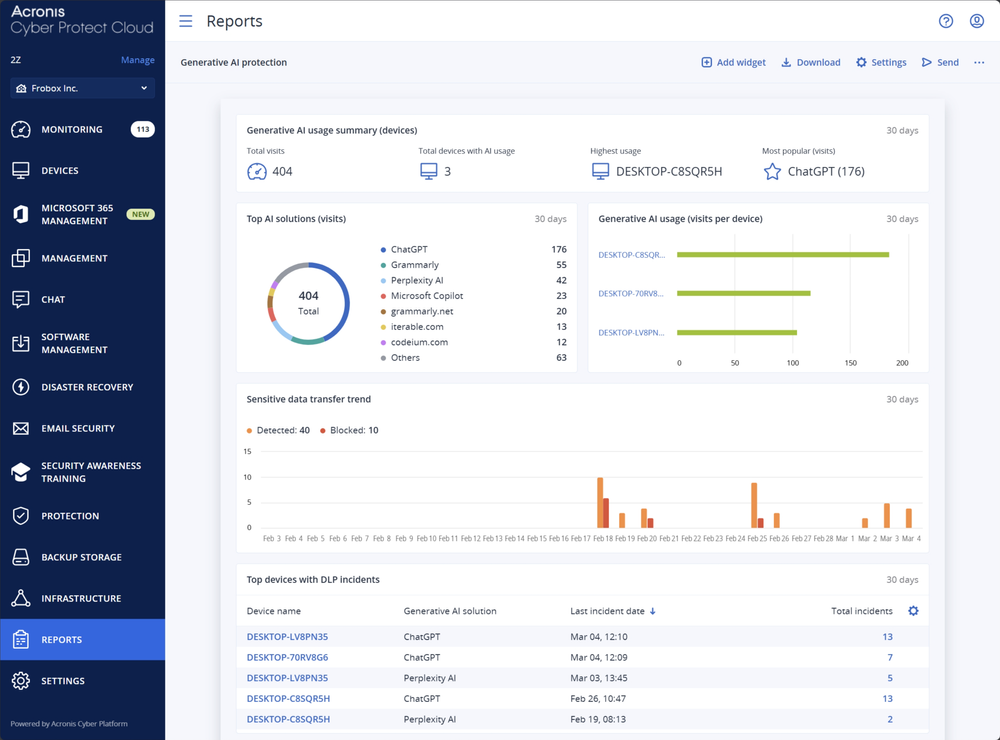
Review AI usage violations and reporting
Log and review AI usage events in detail.
Frequently asked questions about GenAI security

Sorry, your browser is not supported.
It seems that our website is incompatible with your current browser's version. Don't worry, this is easily fixed!
To view our complete website, simply update your browser now or continue anyway.